8 posts tagged with "censorship"

View All Tags

VPN for Wi-Fi Router Setup: A Technical Deep Dive

· 17 min read

In restrictive regions, setting up a VPN on your Wi-Fi router can be your best bet to bypass censorship and access the open internet. But how does it really work? A vpn for wi-fi router setup moves encrypted tunneling from individual devices to the network edge, protecting phones, laptops, smart TVs, consoles, and IoT devices through one router-level connection. This deep dive explains the architecture, protocol choices, firmware options, performance limits, and troubleshooting steps advanced users should understand before deploying a router VPN.

Router-based VPN deployment is powerful, but it is not magic. It depends on router CPU capacity, firmware support, VPN protocol behavior, DNS handling, and the censorship techniques used on the network. Used correctly, it can simplify privacy controls and make censorship circumvention more consistent across a home or small office network.

Understanding VPNs and Wi-Fi routers​

A virtual private network, or VPN, creates an encrypted tunnel between a client and a remote VPN server. Traffic leaving the client is encapsulated, encrypted, and sent to the server. The server then forwards that traffic to its destination on the public internet. Replies return through the same tunnel.

The core functions of a VPN are:

  • Encryption: Prevents local observers, such as public Wi-Fi operators or an ISP, from reading packet contents.
  • Tunneling: Wraps network traffic inside a VPN protocol so it can cross untrusted networks.
  • IP address substitution: Websites and services see the VPN server IP address instead of the client’s public IP.
  • Traffic routing control: Sends selected or all traffic through the tunnel, depending on policy.
  • Integrity protection: Helps prevent tampering with packets in transit.

A Wi-Fi router plays a different role. It is the gateway between your local network and the internet. In a typical home network, the router performs several jobs at once:

  • Creates the wireless LAN using 2.4 GHz, 5 GHz, or 6 GHz radios.
  • Assigns local IP addresses using DHCP.
  • Translates private IP addresses to a public IP using NAT.
  • Applies firewall rules between WAN and LAN.
  • Routes traffic between wired, wireless, guest, and sometimes VLAN-based networks.
  • Provides DNS forwarding or relaying.

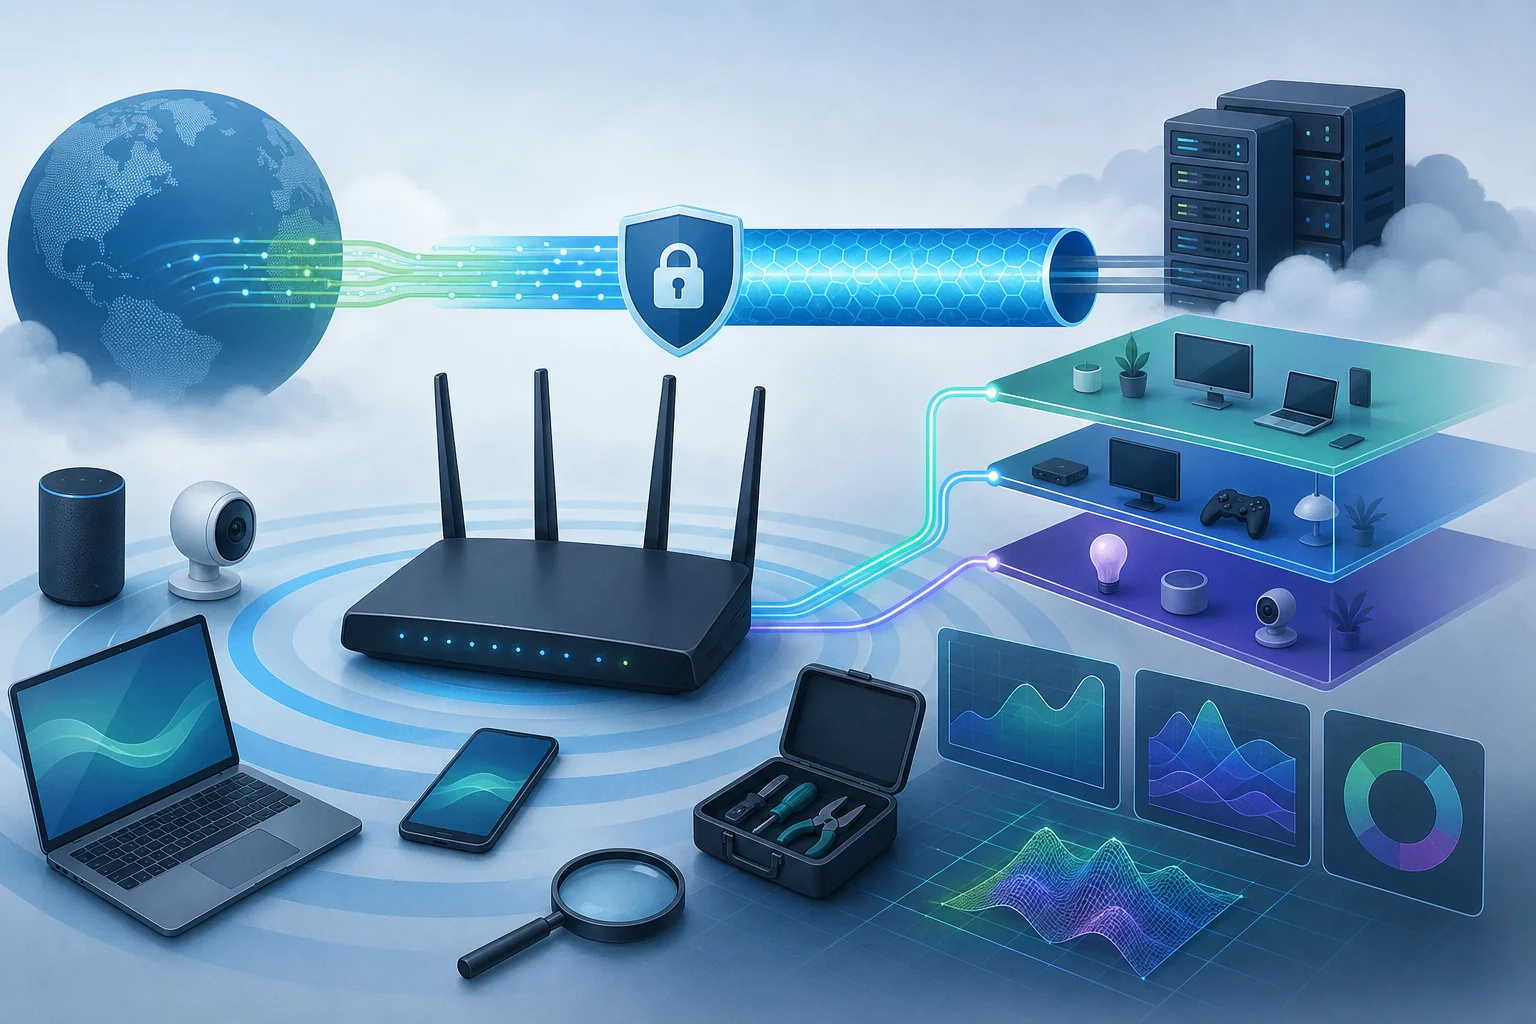
When a VPN runs on a laptop or phone, only that device uses the encrypted tunnel. When a VPN runs on the router, the router becomes the VPN client. Devices behind the router send normal local traffic to the gateway. The router then encrypts and forwards that traffic through the tunnel.

This collaboration changes the privacy model. Instead of installing and maintaining a VPN app on every endpoint, you centralize VPN enforcement at the network boundary. This is especially useful for devices that cannot run VPN apps, such as game consoles, some streaming boxes, older smart TVs, and embedded IoT hardware.
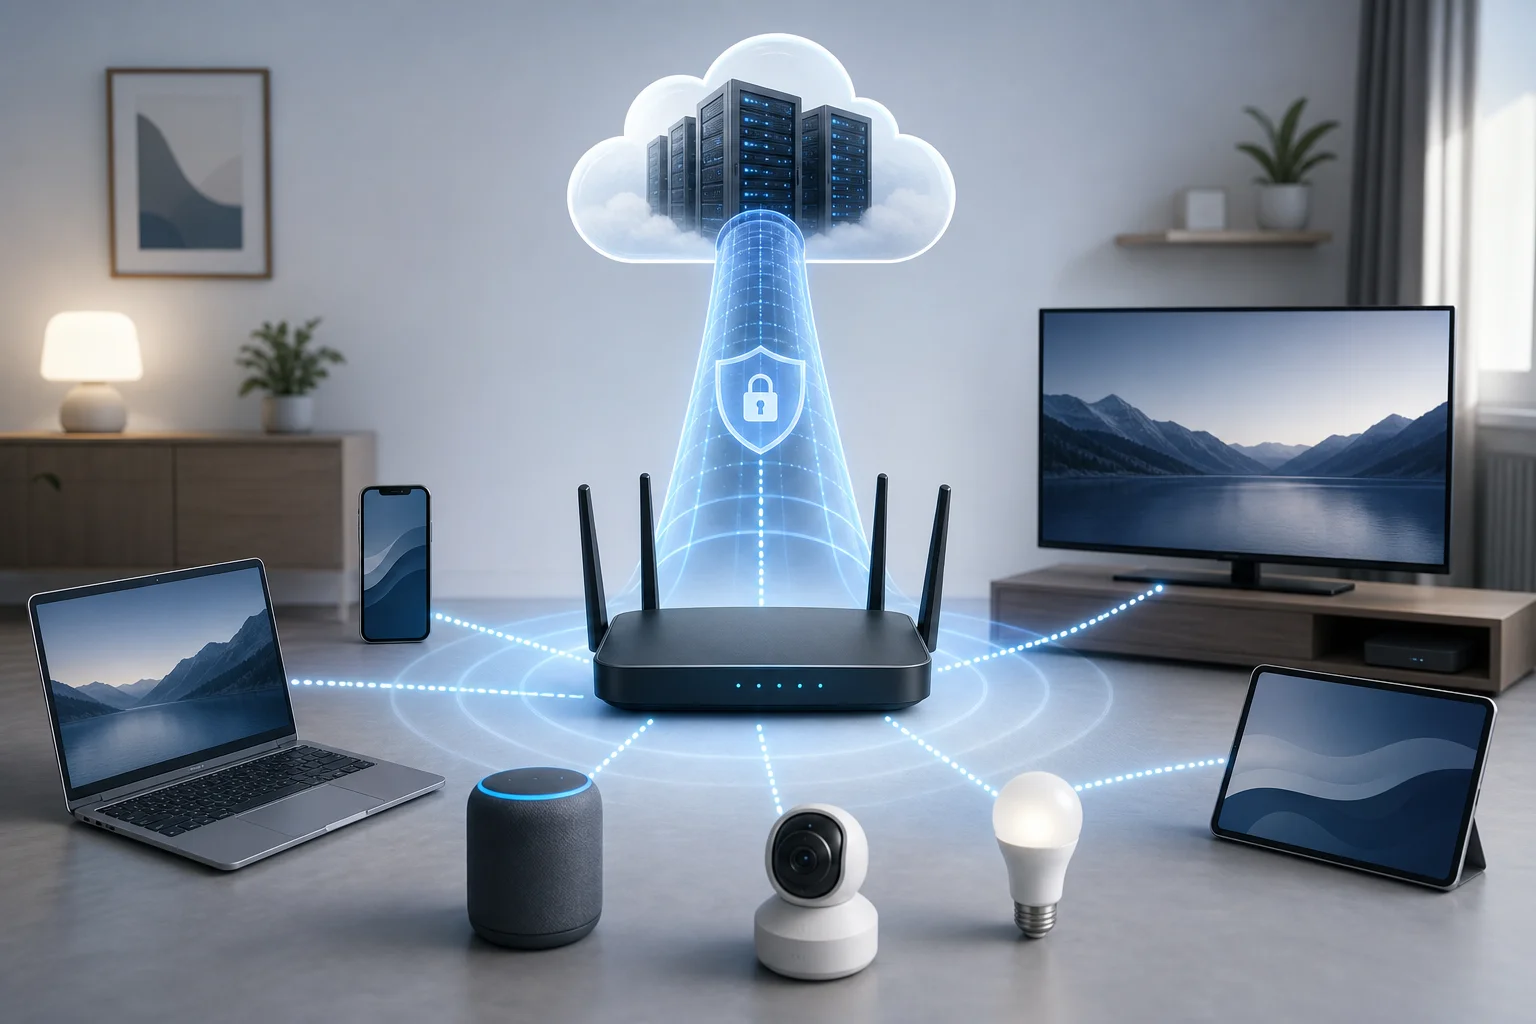
vpn router network diagram

However, router-level VPNs also shift responsibility to the gateway. DNS, firewall rules, split tunneling, kill switch behavior, and firmware updates must be handled carefully. A weak router configuration can leak traffic even when the VPN tunnel appears connected.

Why use a VPN on your Wi-Fi router?​

A router VPN is mainly about coverage, consistency, and control. Instead of depending on users to enable VPN apps correctly, you make encrypted routing the default for the network.

The main advantages include:

  • Network-wide protection: Every device connected to the selected Wi-Fi network can use the VPN tunnel.
  • Support for non-VPN devices: Smart TVs, consoles, and IoT devices can benefit without local VPN clients.
  • Centralized policy: Routing rules, DNS settings, and firewall controls are managed in one place.
  • Reduced setup friction: Guests and secondary devices do not need separate VPN configuration.
  • Location flexibility: You can route traffic through a VPN region that improves access to blocked sites or region-limited content.

For users in restrictive regions, the most important benefit is consistent circumvention. If censorship is implemented through DNS blocking, IP blocking, or basic traffic filtering, a properly configured VPN tunnel can make local network restrictions harder to enforce. The ISP sees an encrypted connection to the VPN server rather than direct connections to blocked destinations.

That said, censorship systems vary. Some networks use deep packet inspection, active probing, VPN server blacklists, or protocol throttling. In those environments, router VPN success depends heavily on the protocol, port, server reputation, and obfuscation capabilities. You should also understand local laws and risks before attempting circumvention.

From a privacy standpoint, a VPN on your router hides destination details from the local ISP, but it does not make you anonymous. The VPN provider can see metadata such as connection times and the VPN server can see traffic leaving toward the internet unless end-to-end encryption, such as HTTPS, also protects it. Browser fingerprinting, account logins, cookies, and device identifiers can still identify you.

Security improves when the VPN is combined with good router hygiene: strong admin passwords, updated firmware, disabled remote management, segmented guest networks, and DNS leak prevention. In other words, a router VPN should be part of a layered network security design, not the whole design.

Step-by-step guide to setting up a VPN on your router​

Before starting, confirm that your router can act as a VPN client. Many consumer routers support VPN server mode, which lets you connect back home from outside, but not VPN client mode, which routes home traffic through a commercial or external VPN provider. Those are different features.

Step 1: Audit your network and router capabilities​

Record your current network settings before changing anything:

  1. Router model and hardware revision.
  2. Current firmware version.
  3. WAN connection type, such as DHCP, PPPoE, static IP, or cellular modem.
  4. LAN subnet, DHCP range, and reserved IP addresses.
  5. DNS configuration.
  6. Existing port forwards, VLANs, guest networks, or parental controls.
  7. ISP modem mode, such as bridge mode or router mode.

Then verify hardware limits. VPN encryption is CPU-intensive. Older routers with low-power MIPS or ARM chips may only handle modest throughput over OpenVPN. Newer routers with AES acceleration, multi-core ARM processors, or WireGuard support usually perform better.

Step 2: Confirm VPN compatibility and firmware options​

Check whether your firmware supports VPN client configuration. Common options include:

Firmware or platformVPN client supportBest fitNotes
Stock AsusWRTOften yesAdvanced home usersGood OpenVPN support on many Asus models
OpenWrtYesTechnical usersHighly flexible, strong package ecosystem
DD-WRTYesLegacy and enthusiast routersModel support varies by build
FreshTomatoYesBroadcom-based routersUseful interface, limited device range
pfSense or OPNsenseYesDedicated firewall appliancesExcellent routing, firewall, and policy controls
MikroTik RouterOSYesNetwork engineersPowerful but requires careful configuration
ISP-provided firmwareOften limitedBasic networksUsually lacks advanced VPN client features

If the stock firmware lacks VPN client support, you may install third-party firmware only if your exact hardware revision is supported. Flashing the wrong image can brick the router. Download firmware from the official project site, verify checksums when available, and keep a recovery method ready.

Step 3: Choose the router VPN topology​

There are three common deployment patterns:

  • Full-tunnel VPN: All LAN traffic exits through the VPN. This is simple and strong for censorship resistance.
  • Split-tunnel VPN: Only selected devices, domains, or destination IP ranges use the VPN. This improves speed and compatibility.
  • Dual-SSID design: One Wi-Fi network routes through the VPN, while another uses the normal ISP path. This is practical for households with mixed needs.

Advanced users often prefer a dual-SSID or VLAN-based design. For example, wifi-vpn can route through the VPN tunnel, while wifi-direct uses the ISP route. This avoids breaking services that reject VPN traffic, such as some banking sites or local streaming platforms.

Step 4: Import VPN credentials and configuration​

Your VPN provider should supply configuration files or manual settings. For OpenVPN, this is usually an .ovpn file plus credentials or certificates. For WireGuard, it is a peer configuration containing private and public keys, endpoint details, and allowed IPs.

Typical OpenVPN parameters include:

  • Server hostname or IP address.
  • Port and transport, such as UDP 1194 or TCP 443.
  • Cipher and authentication settings.
  • CA certificate and client certificate if required.
  • Username and password if used.
  • Redirect gateway option for full-tunnel routing.
  • DNS push options.

Typical WireGuard parameters include:

  • Local private key.
  • Peer public key.
  • Endpoint hostname and port.
  • Allowed IPs, commonly 0.0.0.0/0 and ::/0 for full tunnel.
  • Persistent keepalive, often useful behind NAT.

Store private keys and credentials securely. Anyone with those details may be able to use your VPN account.

Step 5: Configure routing, DNS, and firewall behavior​

After the tunnel connects, routing determines whether traffic actually uses it. For a full-tunnel setup, the default route should point through the VPN interface. For split tunneling, use policy-based routing by source IP, source subnet, VLAN, or destination.

DNS is equally important. If LAN clients still use ISP DNS servers, blocked domain lookups may fail or leak. Configure the router to forward DNS through the VPN or use secure DNS resolvers reachable inside the tunnel. Also block outbound DNS from LAN clients except to the router if you want stricter control.

A basic leak-resistant design includes:

  • DHCP hands out the router IP as DNS server.
  • The router forwards DNS through the VPN tunnel.
  • Firewall rules block LAN-to-WAN DNS on port 53 when VPN policy requires tunneling.
  • IPv6 is either routed through the VPN or disabled if unsupported.
  • A kill switch blocks WAN egress if the VPN tunnel drops.

Step 6: Test the setup before relying on it​

Do not assume the VPN is working because the interface says “connected.” Test from a client device attached to the VPN Wi-Fi network.

Check the following:

  1. Public IP address matches the VPN server, not the ISP.
  2. DNS leak tests show VPN or chosen resolver addresses.
  3. IPv6 does not expose the ISP address.
  4. Blocked sites load as expected.
  5. Non-VPN SSIDs or VLANs still behave as intended.
  6. Throughput and latency are acceptable.
  7. The kill switch works by stopping the VPN process and confirming traffic does not escape through WAN.

Common pitfalls include double NAT from ISP gateways, wrong time settings that break certificate validation, MTU problems that cause partial loading, and DNS settings that are overwritten by WAN renewals. Document every change so you can roll back quickly.
router VPN setup dashboard

Exploring VPN protocols and their impact​

Protocol choice has a direct effect on speed, stability, censorship resistance, and router CPU load. The best option depends on both your hardware and the filtering environment.

OpenVPN​

OpenVPN is mature, widely supported, and highly configurable. It can run over UDP for better performance or TCP for easier traversal of restrictive networks. TCP 443 can resemble normal HTTPS at the port level, although deep packet inspection may still identify it as VPN traffic.

On routers, OpenVPN can be slower than newer protocols because it often runs in user space and may not fully use hardware acceleration. Still, it remains a strong option because many router firmwares support it well.

WireGuard​

WireGuard is lightweight and often much faster than OpenVPN on modern routers. It uses a lean codebase and modern cryptography. Configuration is simple, and roaming behavior is excellent.

The tradeoff is that WireGuard traffic can be easier to fingerprint in some restrictive environments unless the provider adds obfuscation or wraps it in another transport. For raw performance on supported firmware, it is usually one of the best choices.

L2TP/IPSec and IKEv2/IPSec​

L2TP/IPSec is common but older. It can be blocked easily because it uses recognizable ports and protocols. It may also struggle behind strict NAT unless NAT traversal works correctly.

IKEv2/IPSec is more modern and stable for mobile devices, but router support varies. It can be fast when hardware acceleration is available. However, like L2TP/IPSec, it may be easier for restrictive networks to block than highly adaptable OpenVPN configurations.

PPTP​

PPTP should be avoided for security-sensitive use. It is outdated and has known weaknesses. It may still appear in old router interfaces, but it is not suitable for privacy or censorship circumvention.

Protocol recommendations for restrictive regions​

For restrictive regions, prioritize reliability and adaptability:

  • Use OpenVPN over TCP 443 when networks block common VPN ports.
  • Use OpenVPN over UDP when speed matters and UDP is not throttled.
  • Use WireGuard when your provider supports stable endpoints and the network does not aggressively fingerprint it.
  • Consider obfuscated or stealth modes if your VPN provider offers them for router-compatible configs.
  • Avoid PPTP and do not rely on L2TP/IPSec where blocking is common.

Protocol choice also affects MTU. Encapsulation adds overhead, so packets may need a smaller maximum size. Symptoms of MTU problems include sites that partially load, video players that hang, and TLS handshakes that fail. Adjusting MTU or MSS clamping on the router often fixes this.

Technical challenges and solutions in router VPN setup​

Router VPN deployments fail in predictable ways. Most problems come from hardware limits, routing mistakes, DNS leaks, or conflicts between ISP equipment and router firmware.

Common setup and usage issues​

Low throughput is the most common complaint. Encryption may overwhelm the router CPU. Check CPU usage during speed tests. If one core is pinned, the protocol or hardware is the bottleneck.

Tunnel connects but traffic does not pass usually indicates routing or firewall errors. Confirm that default routes, NAT rules, and policy routing tables point to the tunnel interface.

DNS leaks happen when clients use ISP DNS, hardcoded public DNS, or IPv6 DNS outside the tunnel. Block direct DNS egress and force DNS through the router.

Streaming or banking sites fail because some services block VPN IP ranges. Use split tunneling or a direct-access SSID for services that require the ISP path.

Frequent disconnects may be caused by unstable WAN, blocked keepalives, overloaded routers, or VPN server congestion. Try another server, change transport, or tune keepalive settings.

IPv6 leaks occur when IPv4 is tunneled but IPv6 remains routed through the ISP. Either configure IPv6 through the VPN or disable IPv6 on the VPN network.

Solutions for better performance​

Start with protocol selection. If available, test WireGuard and OpenVPN UDP before OpenVPN TCP. TCP-over-TCP tunneling can create poor performance under packet loss because both layers retransmit.

Next, optimize routing. Policy-based routing reduces unnecessary VPN load. For example, route only sensitive devices or specific VLANs through the VPN. Keep latency-sensitive local traffic, such as gaming or local media, on the direct path if privacy requirements allow it.

Then tune packet size. If you suspect fragmentation, lower tunnel MTU or enable MSS clamping. Common VPN MTU values vary by protocol and WAN type, so test rather than copy blindly.

Hardware may also be the limiting factor. For sustained high-speed VPN use, consider:

  • A router with strong ARM CPU and AES acceleration.
  • A mini PC running pfSense, OPNsense, or OpenWrt.
  • A dedicated VPN gateway behind your existing router.
  • VLAN-capable switches and access points for cleaner segmentation.

Best practices for security and speed​

Use a security baseline before enabling the VPN:

  • Change default router admin credentials.
  • Disable WAN-side administration unless strictly needed.
  • Update firmware regularly.
  • Back up router configuration after successful setup.
  • Use strong Wi-Fi encryption, preferably WPA2-AES or WPA3.
  • Separate IoT devices from trusted laptops and phones.
  • Apply least-privilege firewall rules between VLANs.
  • Monitor logs for tunnel drops and authentication failures.

For speed, keep the configuration simple. Avoid stacking multiple VPN tunnels unless you understand the latency and MTU impact. Choose nearby VPN servers when censorship bypass does not require a distant region. Finally, schedule periodic tests because VPN servers, ISP routes, and blocking patterns change over time.
VPN performance troubleshooting

Common misconceptions about VPNs and routers​

Router VPN setups are often misunderstood. The following FAQ-style answers clarify the most common assumptions advanced users should challenge.

Does a VPN on my router make every device anonymous?​

No. It changes the public IP address seen by websites and encrypts traffic between your router and the VPN server. It does not remove browser fingerprints, account logins, cookies, device telemetry, or tracking pixels. Use privacy-focused browser settings, compartmentalized accounts, and end-to-end encryption when anonymity matters.

Will any Wi-Fi router work with a VPN?​

No. The router must support VPN client mode, and it must be powerful enough for the throughput you need. Some routers advertise “VPN support” but only provide VPN server features. Always confirm client support for the protocol you plan to use.

Is router VPN performance the same as using a VPN app?​

Usually not. Phones and laptops often have faster CPUs and optimized VPN apps. Routers may have weaker processors and limited cryptographic acceleration. WireGuard on capable hardware can be fast, but OpenVPN on older routers may be much slower.

Can a VPN always bypass censorship?​

No. A VPN can bypass many forms of filtering, especially DNS and basic IP blocking. However, advanced censorship can block known VPN servers, fingerprint protocols, throttle encrypted tunnels, or disrupt handshakes. Obfuscation, alternate ports, and server rotation may be needed.

Does a router VPN protect me from malicious websites?​

Not by itself. A VPN encrypts transport between you and the VPN server. It does not automatically block phishing, malware, unsafe downloads, or compromised websites. Use secure DNS filtering, browser protections, endpoint security, and careful browsing habits.

Should I disable IPv6 when using a router VPN?​

If your VPN and router do not support IPv6 tunneling correctly, disabling IPv6 on the VPN-routed network may prevent leaks. If you need IPv6, configure it deliberately and test it with leak-checking tools.

Final considerations for advanced users​

Before deploying a VPN on a Wi-Fi router, review your actual network requirements. Ask what must be protected, what must be fast, and what must remain compatible with local services. A full-tunnel setup is simpler, but it may not be ideal for every device. A segmented design with VPN and non-VPN SSIDs often gives better operational control.

Plan for ongoing management. Keep copies of working configurations, certificates, keys, and firmware images in a secure location. Track which devices use the VPN route. Check DNS and IP leaks after firmware upgrades. Review logs when connectivity changes. If users depend on uncensored access, configure fail-closed firewall behavior so traffic does not silently fall back to the ISP path.

Future-proofing matters because restrictions evolve. Choose firmware with active maintenance, protocols with strong community support, and a VPN provider that offers multiple connection methods. Where possible, use routers or firewall appliances that support WireGuard, OpenVPN, VLANs, policy routing, custom firewall rules, and DNS control. This gives you room to adapt when a protocol is blocked or a server range becomes unreliable.

A well-designed router VPN setup can provide durable, network-wide privacy and more reliable access in restrictive regions. It works best when treated as an engineered system: tested, monitored, documented, and tuned. Equip your Wi-Fi router with BeFreeVPN to effortlessly bypass censorship and enjoy a secure, registration-free browsing experience.
Setting up a VPN for Google TV: a deep dive

· 19 min read

Are you looking to bypass regional restrictions and secure your streaming on Google TV? This in-depth guide examines the technical steps necessary to set up a VPN effectively. If you need a vpn for google tv setup in a restrictive region, the goal is not only smoother access to apps and media. It is also to reduce exposure to network surveillance, ISP throttling, DNS filtering, and content blocking while keeping your streaming device stable and fast.

Google TV is built on Android TV, which makes VPN deployment more flexible than on many smart TV platforms. However, censorship-heavy networks, weak routers, app-store restrictions, and protocol blocking can complicate the process. This guide covers the technical choices, setup paths, performance tuning, privacy controls, misconceptions, and advanced bypass methods you should understand before relying on a VPN for streaming or censorship circumvention.

vpn for google tv setup overview

1. Introduction to VPNs for Google TV​

A VPN, or virtual private network, creates an encrypted tunnel between your Google TV device and a remote VPN server. Instead of sending traffic directly through your ISP or local network operator, your traffic is wrapped inside an encrypted connection and exits through the VPN provider’s server.

For Google TV users in open internet environments, this may mainly improve privacy or help access region-specific streaming libraries. In restrictive regions, the role is more serious. A VPN can help route traffic around blocks, reduce DNS manipulation, and make it harder for local intermediaries to inspect what services you are using.

Why use a VPN on Google TV in restrictive regions​

Restrictive networks often use a mix of blocking methods. These may include DNS poisoning, IP blocking, deep packet inspection, app-store filtering, or throttling of known streaming endpoints. Google TV depends on cloud services, app updates, streaming APIs, and DNS lookups, so even partial censorship can break the experience.

A VPN can help by:

  • Encrypting traffic between Google TV and the VPN server.
  • Replacing local DNS resolution with VPN-controlled DNS.
  • Masking your visible IP address from streaming platforms and websites.
  • Routing around local ISP blocks and network firewalls.
  • Reducing some forms of traffic classification and throttling.

However, a VPN is not magic. If the VPN protocol itself is blocked, if the VPN app is removed from the local Play Store, or if streaming services flag a crowded VPN server, you may need advanced configuration.

Benefits of VPNs for streaming and privacy​

The main benefits of a VPN on Google TV are practical:

  1. Streaming access: You can connect through a server in a supported country to access apps or libraries available in that region.
  2. Network privacy: Your ISP sees that you are connected to a VPN server, but not the exact streaming domains or media requests inside the encrypted tunnel.
  3. Safer public or shared networks: If your Google TV is connected in a hotel, dorm, office apartment, or shared housing setup, a VPN reduces local network exposure.
  4. DNS integrity: A good VPN forces DNS queries through encrypted or provider-controlled resolvers, helping prevent DNS hijacking.
  5. Consistency: With a stable server and protocol, you may avoid inconsistent routing caused by local ISP filtering.

Challenges faced without a VPN​

Without a VPN, Google TV traffic is usually visible to multiple parties: the ISP, Wi-Fi administrator, DNS provider, and in some cases regional network gateways. In restrictive regions, this can lead to blocked apps, interrupted streams, failed logins, and app-store access problems.

You may also see symptoms that look like device problems but are actually network interference:

  • Streaming apps load but videos never start.
  • Play Store search results are incomplete.
  • Google services work intermittently.
  • DNS errors appear only on certain apps.
  • Streams downgrade quality despite a fast connection.
  • Specific foreign news, education, or entertainment apps fail.

A correct VPN configuration can solve many of these issues, but the protocol and setup method matter.

2. Understanding VPN Protocols and Mechanisms​

The VPN protocol controls how your encrypted tunnel is built, authenticated, maintained, and transported across the network. In restrictive regions, protocol choice can determine whether the VPN connects at all.

Common VPN protocols for Google TV​

ProtocolStrengthsWeaknessesBest use case on Google TV
OpenVPN UDPMature, widely supported, configurableCan be detected or throttled; may need extra obfuscationFlexible setup, manual configuration, restrictive networks with custom ports
OpenVPN TCPMore reliable on unstable networks; can use port 443Slower than UDP due to TCP-over-TCP overheadNetworks that block UDP or allow only web-like traffic
IKEv2/IPsecFast reconnection, good for mobile networksEasier to block in some regions; app support variesStable home networks or ISP connections without aggressive filtering
WireGuardVery fast, modern cryptography, low overheadDistinct traffic pattern; may be blocked without obfuscationHigh-speed streaming where censorship is moderate
Proprietary stealth protocolsDesigned to hide VPN signaturesLess transparent; depends on provider implementationHigh-censorship environments where standard protocols fail

For a VPN for Google TV setup, OpenVPN and WireGuard are common because many Android TV VPN apps support them. Still, stealth or obfuscated modes may be necessary where VPN blocking is aggressive.

How protocols help bypass censorship​

Censorship systems usually look for one or more signals:

  • Destination IP addresses linked to banned services.
  • DNS requests for blocked domains.
  • Traffic signatures that match VPN protocols.
  • TLS handshake metadata or server name indications.
  • Unusual packet timing or connection behavior.

VPN protocols help by encrypting content and tunneling requests through another server. Obfuscation goes further. It attempts to make VPN traffic look like ordinary HTTPS or another permitted protocol. For example, OpenVPN over TCP port 443 may resemble standard encrypted web traffic at a basic firewall level. More advanced stealth systems wrap or disguise VPN packets to reduce protocol fingerprinting.

Considerations for choosing the right protocol​

Choose based on your threat model and network constraints:

  • For speed: Start with WireGuard or OpenVPN UDP.
  • For reliability: Try IKEv2 or OpenVPN TCP.
  • For restrictive networks: Use OpenVPN TCP on port 443, stealth mode, or a provider-specific obfuscated protocol.
  • For privacy: Prefer providers with strong encryption, leak protection, and clear no-logs policies.
  • For compatibility: Confirm the provider has an Android TV or Google TV app, or supports router-level setup.

Also consider whether your Google TV device has enough CPU headroom. Entry-level devices may struggle with high-bitrate 4K streaming over heavy encryption, especially with OpenVPN.

3. Step-by-Step VPN Setup for Google TV​

There are three main ways to set up a VPN on Google TV: install a VPN app directly, sideload an Android APK, or configure the VPN on your router. Direct installation is simplest. Router configuration is stronger when the device cannot run the VPN app or when you want all traffic covered.

google tv vpn configuration steps

Pre-installation requirements and considerations​

Before you start, verify the following:

  • Your Google TV device is updated to the latest available system version.
  • You have a stable internet connection.
  • Your Google account can access the Play Store, or you have a safe APK source.
  • Your VPN provider supports Android TV, Google TV, OpenVPN, WireGuard, or router setup.
  • You know which region or server you need.
  • You understand local rules and risks related to VPN use in your jurisdiction.

If you are in a restrictive region, download required apps, configuration files, and backup APKs before traveling or before blocks become active. Store OpenVPN .ovpn files and credentials securely.

Method 1: Install a VPN app from Google Play on Google TV​

This is the preferred method when available.

  1. Open Google TV Home. Use the remote to navigate to the top menu.
  2. Go to Apps. Open the app search function.
  3. Search for your VPN provider. Use the exact provider name to avoid clones.
  4. Install the official app. Check the developer name before installing.
  5. Open the VPN app. Sign in or activate according to the provider’s process.
  6. Choose a server. Select a location close to your target content region or a nearby low-latency server.
  7. Select a protocol. Start with WireGuard or OpenVPN UDP. If blocked, switch to OpenVPN TCP or stealth mode.
  8. Approve the VPN connection request. Android TV will show a system prompt.
  9. Test streaming and DNS. Open your target app and check whether content loads correctly.

This setup gives you device-level protection. Only Google TV traffic goes through the VPN, not your entire home network.

Method 2: Sideload a VPN APK​

If the VPN app is not available in your Play Store region, sideloading may work. Use caution because malicious APKs are common.

  1. Install a trusted file manager from the Play Store.
  2. Download the APK from the VPN provider’s official website on another device.
  3. Transfer it by USB drive, cloud storage, or local network share.
  4. On Google TV, enable installation from unknown sources for the file manager.
  5. Open the APK and install it.
  6. Disable unknown-source permission after installation.
  7. Launch the VPN app and connect.

Only sideload APKs from official sources. Avoid modified apps, cracked VPN clients, or unofficial mirrors. They can leak data or contain malware.

Method 3: Configure VPN on your router​

Router-level VPN is useful when the Google TV app cannot connect, when you want network-wide coverage, or when you want to use custom OpenVPN/WireGuard configs.

General steps:

  1. Confirm your router supports VPN client mode. Many ISP routers do not.
  2. Install compatible firmware if needed, such as OpenWrt, DD-WRT, AsusWRT-Merlin, or vendor VPN firmware.
  3. Download the VPN configuration files from your provider.
  4. Upload OpenVPN or WireGuard settings to the router.
  5. Enter credentials, certificates, keys, and DNS settings.
  6. Route your Google TV through the VPN tunnel.
  7. Test for IP and DNS leaks from another device on the same network.
  8. Connect Google TV to that router or VPN-enabled Wi-Fi network.

Advanced users may prefer policy-based routing. This sends only Google TV through the VPN while keeping gaming consoles, smart home devices, or local services outside the tunnel.

Troubleshooting common setup issues​

VPN app installs but will not connect. Switch protocols. Try OpenVPN TCP port 443, stealth mode, or another server. Check whether your network blocks UDP.

Streaming app detects the VPN. Change servers, clear app cache, restart Google TV, and avoid overloaded locations. Some platforms block known VPN IP ranges.

Internet stops after connecting. Check DNS settings, kill switch behavior, and router firewall rules. If using router VPN, verify default gateway and NAT rules.

VPN connects but location does not change. Force stop the streaming app. Clear cache. Confirm the VPN server IP geolocates to the expected country.

Remote navigation is broken in sideloaded app. Some mobile Android VPN apps are not optimized for TV. Use a Bluetooth mouse, remote-control app, or provider with Android TV support.

Captive portal blocks VPN. Hotels and shared networks may require browser login before VPN traffic is allowed. Authenticate first, then connect the VPN.

4. Optimizing VPN Performance on Google TV​

A working VPN is not always an optimized VPN. Streaming requires consistent throughput, low packet loss, and stable DNS. In restrictive regions, a slow but stable stealth connection may be better than a fast protocol that disconnects often.

Techniques to enhance VPN speed and connection quality​

Start with the basics:

  • Use Ethernet instead of Wi-Fi where possible.
  • If using Wi-Fi, prefer 5 GHz or 6 GHz over congested 2.4 GHz.
  • Place the router near the Google TV device.
  • Close unused background apps.
  • Restart the VPN app after changing protocol.
  • Keep Google TV firmware and VPN app updated.

Then tune the VPN:

  • Try WireGuard for speed if it is not blocked.
  • Try OpenVPN UDP for a balance of compatibility and performance.
  • Reduce encryption overhead only if the app safely supports it; do not disable encryption.
  • Use split tunneling for non-sensitive apps if available.
  • Avoid distant servers unless required for a specific content region.

Adjusting settings for optimal streaming experience​

For 4K streaming, stability matters more than peak speed. A VPN that spikes to high bandwidth but drops packets will buffer. Use these settings where available:

  • Auto-connect on boot: Ensures Google TV is protected before apps launch.
  • VPN kill switch: Blocks traffic if the tunnel drops, reducing accidental exposure.
  • DNS leak protection: Forces DNS through the VPN.
  • Protocol fallback: Lets the app switch if one protocol fails.
  • Split tunneling: Routes only selected apps through the VPN.

If your provider supports app-based split tunneling, route streaming apps, browser apps, and blocked services through the VPN. Leave local media servers or LAN apps outside the tunnel if they need local discovery.

Impact of server selection on performance​

Server selection affects latency, throughput, detection risk, and reliability. A nearby server is usually faster, but a target-country server may be required for regional content. In restrictive areas, some nearby countries have better peering and less packet loss than distant popular locations.

Use this decision path:

  1. Need a specific streaming region? Choose that country first.
  2. Multiple cities available? Test the least crowded or closest city.
  3. Connection blocked? Switch to stealth-supported servers.
  4. Speeds unstable? Try a nearby country with better routing.
  5. VPN detected? Rotate to another server or residential-style location if offered.

Avoid assuming that the most popular server is best. Popular servers can be overloaded and more likely to appear on blocklists.

5. Ensuring Privacy and Security on Google TV​

A VPN protects the network path, but Google TV privacy also depends on account settings, app permissions, DNS behavior, and device hygiene. Advanced users should treat the VPN as one layer in a broader security model.

How VPNs protect data and identity​

A VPN can protect against local network observation by encrypting traffic from Google TV to the VPN server. This helps hide app traffic patterns from Wi-Fi operators and ISPs. It also replaces your public IP address with the VPN server’s IP address when you access remote services.

However, a VPN does not make you anonymous by itself. Streaming accounts, Google account activity, device identifiers, cookies, and payment methods can still identify you. If you log in to a personal account, the service knows it is you, even if your network location changes.

Additional security settings on Google TV​

Review these Google TV settings:

  • Disable installation from unknown sources after sideloading.
  • Remove unused apps and old APK installers.
  • Review app permissions, especially location, microphone, and storage.
  • Turn off personalized recommendations if privacy is more important than convenience.
  • Keep automatic updates enabled when possible.
  • Use a separate Google account for high-risk travel or restrictive environments.
  • Disable Bluetooth pairing when not needed.

If your VPN app has a kill switch or always-on VPN option, enable it. On some Android TV builds, always-on VPN options may be limited compared with phones. Test behavior by disconnecting the VPN and confirming whether traffic is blocked or allowed.

Best practices for maintaining privacy​

Use a privacy routine:

  1. Connect the VPN before opening restricted apps.
  2. Verify the server location if access matters.
  3. Clear app cache after changing regions.
  4. Avoid logging into sensitive accounts over unknown networks without VPN protection.
  5. Keep backup servers and protocols ready.
  6. Do not install unofficial streaming or VPN apps from random sources.
  7. Recheck settings after firmware updates.

Also, separate goals. If your goal is censorship circumvention, prioritize stealth and reliability. If your goal is streaming quality, prioritize low latency and server reputation. If your goal is privacy, prioritize leak protection and account compartmentalization.

6. Common Misconceptions About VPNs on Google TV​

VPNs are powerful tools, but overestimating them can create false confidence. It is better to understand their limits before depending on them in a restrictive region.

Misbeliefs about VPN effectiveness in restrictive regions​

Misconception: Any VPN will bypass censorship.
Not true. Some VPNs use easily detected protocols or blocked server ranges. In strict networks, you may need obfuscation, rotating servers, TCP 443 support, or router-based configuration.

Misconception: A VPN guarantees access to every streaming service.
Streaming platforms can block data-center IPs or enforce account-region rules. A VPN improves routing options, but it does not guarantee availability.

Misconception: Once installed, it will always work.
Censorship systems change. Servers get blocked. Apps update. Keep multiple protocols and server locations ready.

Explaining bandwidth issues and server load​

When users blame the VPN for slow streaming, the cause may be one of several layers:

  • Local Wi-Fi interference.
  • ISP throttling or congestion.
  • Long-distance routing to the VPN server.
  • Overloaded VPN server.
  • Weak Google TV hardware.
  • Heavy encryption overhead.
  • Streaming platform rate limits.

Test systematically. Compare speeds with and without VPN. Test several servers. Try Ethernet. Change protocols. If only one streaming app is slow, the issue may be platform-specific rather than VPN-wide.

Clarifying the myth that VPN usage is illegal​

VPN legality depends on jurisdiction. In many countries, VPN use is legal for privacy, remote work, and security. In some restrictive regions, VPN access may be regulated, limited to approved providers, or risky in certain contexts.

The key point is this: VPN technology itself is not inherently illegal, but how and where it is used can matter. Before using a VPN to bypass censorship, review local laws and understand potential consequences. This article provides technical information, not legal advice.

FAQ: Common questions about VPN for Google TV setup​

Can I install a VPN directly on Google TV?​

Yes. If the VPN provider offers an Android TV or Google TV app, install it from the Play Store, sign in, choose a server, and approve the VPN connection prompt.

What is the best VPN protocol for Google TV streaming?​

WireGuard is often fastest, while OpenVPN UDP is widely compatible. In restrictive regions, OpenVPN TCP on port 443 or a stealth protocol may work better.

Should I use a router VPN instead of a Google TV app?​

Use a router VPN if the app is unavailable, blocked, or unstable. Router setup also protects all selected devices, but it requires more technical configuration.

Will a VPN stop buffering on Google TV?​

Not always. A VPN may reduce throttling or routing problems, but it can also add overhead. Choose nearby servers, use Ethernet, and test protocols for the best result.

7. Advanced Tips for Bypassing Censorship​

Advanced censorship circumvention requires flexibility. Do not depend on one protocol, one server, or one installation method. Prepare fallback options before you need them.

stealth vpn censorship bypass

Using stealth VPN features to avoid detection​

Stealth VPN features are designed to reduce VPN fingerprinting. Depending on the provider, they may be called obfuscation, camouflage mode, stealth mode, bridge mode, or anti-censorship mode.

Useful tactics include:

  • Running OpenVPN over TCP port 443.
  • Using obfuscated servers designed for restrictive networks.
  • Switching to provider-specific stealth protocols.
  • Avoiding default VPN ports that are easy to block.
  • Using DNS leak protection to prevent local resolver exposure.

In high-censorship regions, test stealth servers at different times of day. Some networks apply heavier filtering during political events, exams, protests, or major broadcasts.

Insights into split tunneling and its benefits​

Split tunneling lets you choose which apps use the VPN. On Google TV, this can improve performance and reduce detection risk. For example, you may route a streaming app and browser through the VPN while leaving local media playback outside it.

Benefits include:

  • Lower VPN bandwidth usage.
  • Better performance for apps that do not need the VPN.
  • Fewer issues with local network discovery.
  • Reduced chance of triggering fraud checks on unrelated apps.

However, split tunneling can also create leaks if misconfigured. If privacy is critical, route all traffic through the VPN and enable a kill switch. If performance is the priority, split only low-risk apps outside the tunnel.

Case studies of successful VPN usage in restricted zones​

Consider these realistic scenarios:

Scenario 1: App store filtering.
A traveler in a restrictive region cannot find the VPN app in the Play Store on Google TV. They download the official APK before travel, sideload it, enable stealth mode, and connect over TCP 443. The app then works without relying on local app-store availability.

Scenario 2: UDP blocking.
A home ISP blocks or throttles UDP VPN traffic. WireGuard and OpenVPN UDP fail. Switching to OpenVPN TCP resolves connection failures, although speed drops slightly. For streaming HD content, the stable TCP tunnel performs better than unstable UDP.

Scenario 3: Streaming service VPN detection.
A user connects to a popular server and the streaming app blocks playback. They clear the app cache, switch to a less crowded city in the same country, and reconnect before launching the app. Playback resumes because the new server IP is not flagged.

Scenario 4: Router-level resilience.
A Google TV device cannot run a VPN app reliably after an update. The user configures WireGuard on an OpenWrt router and uses policy-based routing for the TV only. This restores VPN coverage while keeping other household devices on the normal connection.

These examples show why a strong vpn for google tv setup is not just about installing an app. It is about building a resilient configuration with multiple fallback paths.

Conclusion: Build a resilient VPN setup for Google TV​

A reliable VPN for Google TV requires the right protocol, a clean installation method, careful server selection, and ongoing privacy discipline. In restrictive regions, add stealth features, backup servers, APK access, router options, and split tunneling where appropriate. Start simple with the official Google TV app if available, then move to sideloading or router configuration when censorship, detection, or performance issues demand it.

Discover the simplicity and security of BeFreeVPN, a free, no-registration VPN that works seamlessly with Google TV to help you bypass censorship effortlessly.

VPN for laptop download: a deep dive into advanced options

· 16 min read

In a world where internet freedom is increasingly curtailed, a VPN for laptop download can be your key to uncensored access—especially crucial for those in restrictive regions. This guide explains how laptop VPNs work, which protocols matter, how to install them securely, and what advanced users should check before trusting any provider. It also addresses legal limits, common myths, and practical ways to strengthen privacy beyond the VPN tunnel.

A laptop is often the main device for work, study, research, and cross-border communication. That makes VPN selection more than a convenience choice. In censorship-heavy environments, the wrong protocol, weak DNS handling, or a poorly implemented kill switch can expose traffic at the worst time. The goal is not just to “download a VPN.” The goal is to choose, verify, and operate one with a clear threat model.

vpn for laptop download in restrictive regions

1. Understanding the Need for VPNs in Restrictive Regions​

Internet censorship can take many forms. Some governments block news sites, messaging apps, search engines, cloud storage, or social networks. Others use keyword filtering, DNS poisoning, IP blocking, deep packet inspection, or throttling to make certain services unreliable. In some regions, access may change during elections, protests, conflicts, or public emergencies.

For users, the effects are direct. Students may lose access to research platforms. Journalists may be unable to contact sources. Remote workers may be locked out of productivity tools. Families may struggle to communicate across borders. Even when a site is not fully blocked, slow or unstable access can make it unusable.

A VPN helps by creating an encrypted tunnel between your laptop and a remote VPN server. Your internet service provider can usually see that you are connecting to a VPN endpoint, but it cannot read the contents of your traffic inside the tunnel. Websites and apps see the VPN server’s IP address instead of your local IP address. As a result, a VPN can help bypass regional restrictions when the VPN server is located in a less restricted network environment.

However, a VPN is not magic. It does not remove all risks. Local laws still apply, and the legal status of VPN use differs by country. In some places, VPNs are legal for business and privacy. In others, only approved providers are allowed. Some regions restrict or penalize circumvention tools. Before using a VPN in a restrictive country, review current local rules and assess personal risk. This article is technical guidance, not legal advice.

Ethically, VPNs can support access to information, secure communication, and basic privacy. They can also be misused. Advanced users should focus on legitimate purposes: protecting sensitive data, reaching open information sources, and securing communications on hostile networks.

2. Key Protocols Behind VPN for Laptop Download​

The protocol is the engine of a VPN connection. It defines how encryption, authentication, routing, and session management work. For laptop users, the main choices are OpenVPN, IKEv2/IPsec, and WireGuard. Each has strengths and trade-offs.

OpenVPN​

OpenVPN is one of the most established VPN protocols. It uses the OpenSSL library and can run over UDP or TCP. UDP is usually faster and better for normal browsing, streaming, and calls. TCP can be useful when networks block or degrade UDP, although TCP-over-TCP may cause performance issues on unstable links.

OpenVPN is popular in restrictive regions because it is flexible. It can run on common ports such as TCP 443, the same port used by HTTPS. This may help traffic blend with normal encrypted web traffic, although advanced filtering systems can still detect OpenVPN patterns. Some providers add obfuscation layers to make OpenVPN harder to fingerprint.

Security depends on configuration. Strong cipher suites, certificate validation, and modern TLS settings are essential. Poorly configured OpenVPN can be weaker than its reputation suggests.

IKEv2/IPsec​

IKEv2/IPsec is known for fast reconnection. It is useful on laptops that switch between Wi-Fi networks, mobile hotspots, and sleep states. When the network changes, IKEv2 can often restore the tunnel quickly.

It is generally secure when implemented with strong algorithms. It is also supported by many operating systems, sometimes with native clients. That reduces the need for extra software in some enterprise setups.

The downside is censorship resistance. IKEv2/IPsec uses ports and traffic patterns that may be easier to block in some environments. If a country or network blocks IPsec traffic broadly, IKEv2 may fail even when other protocols work.

WireGuard​

WireGuard is modern, lean, and fast. Its codebase is smaller than older VPN protocols, which can help security auditing. It uses modern cryptographic primitives and is often efficient on laptops, including older hardware.

For speed, WireGuard is usually a strong choice. It can reduce latency and CPU usage compared with older setups. This makes it attractive for video calls, large downloads, and remote work.

For censorship-heavy regions, the picture is mixed. Standard WireGuard traffic can be recognizable. It also uses UDP by default. If the network blocks UDP or fingerprints WireGuard, the connection may fail. Some providers solve this with obfuscation, TCP wrapping, or custom stealth modes. Without those layers, WireGuard may be fast but not always the best for hostile networks.

Protocol Comparison Table​

ProtocolSpeedSecurityCompatibilityCensorship resistanceBest use case
OpenVPN UDPGoodHigh if configured wellVery broadModerate to high with obfuscationGeneral use in restrictive regions
OpenVPN TCP 443ModerateHigh if configured wellVery broadOften better on locked-down networksNetworks that block UDP
IKEv2/IPsecGood to very goodHigh with strong settingsStrong native OS supportLow to moderateRoaming between networks
WireGuardVery highHigh with modern designBroad and growingModerate unless obfuscatedSpeed-focused laptop use

For advanced users in restrictive regions, the best VPN for laptop download is often one that supports more than one protocol. If WireGuard is blocked, switch to OpenVPN TCP. If a captive Wi-Fi network breaks OpenVPN UDP, test IKEv2 or a stealth mode. Flexibility matters.

vpn protocols for laptop security

3. How to Download and Install a VPN on Your Laptop​

Downloading a VPN in a restricted environment requires care. Fake installers, cloned websites, and tampered packages are common risks. Use a clean process and verify what you install.

Step-by-Step VPN Download and Installation Guide​

  1. Define your threat model. Decide what you need most: censorship bypass, privacy from local networks, protection on public Wi-Fi, or stable access to work tools. Your choice of protocol and provider should match that risk.

  2. Use the official source. Download the VPN app from the provider’s official website or trusted app store. Avoid third-party download portals. They may bundle unwanted software or outdated clients.

  3. Check domain authenticity. Look for HTTPS, correct spelling, and a valid certificate. Be alert for lookalike domains, especially if the VPN is popular in your region.

  4. Verify the installer when possible. Advanced users should check digital signatures, hashes, or package signatures. On Windows, inspect the publisher signature. On macOS, check notarization. On Linux, prefer signed repositories or verified packages.

  5. Install with least surprise. Read permission prompts. A VPN client needs network extension or adapter rights, but it should not request unrelated access such as browser passwords or document folders.

  6. Choose the right protocol. Start with the provider’s recommended protocol. If censorship blocks it, try OpenVPN TCP 443, an obfuscated mode, or another supported option.

  7. Enable security controls before browsing. Turn on the kill switch, DNS leak protection, and auto-connect on untrusted networks. Test them before relying on the VPN.

  8. Run a leak test. Check your public IP address, DNS resolver, and WebRTC behavior. If your ISP DNS still appears, fix settings before using sensitive sites.

Secure Installation on Windows, macOS, and Linux​

On Windows, install from a signed executable or Microsoft Store listing if available. Avoid running installers as administrator unless required. After setup, check that the VPN network adapter is created by the expected vendor. Also review startup entries so you know what launches at boot.

On macOS, use apps that are notarized and distributed through the official site or App Store. macOS may ask for permission to add VPN configurations or network extensions. Confirm that the provider name matches. If the app uses a system extension, keep it updated.

On Linux, prefer repository-based installation when offered. Signed APT, RPM, Flatpak, or Snap packages reduce tampering risk. If you import a repository key, confirm the fingerprint from the provider’s official documentation. For manual OpenVPN or WireGuard configs, protect private keys with correct file permissions.

Troubleshooting Download and Installation Issues​

If the VPN website is blocked, try a mirror link from the provider, a trusted app store, or a secure connection from another network. Some users keep offline installers on encrypted storage before traveling to restrictive regions.

If installation fails, remove older VPN drivers, reboot, and reinstall. Conflicts can occur when several VPN apps compete for routing and DNS control. If connections fail after installation, test a different protocol and server. Also check local firewalls, corporate endpoint tools, and captive portals.

If speeds are unusable, switch from TCP to UDP when possible, choose a nearby server, or test WireGuard. If the connection drops under censorship pressure, try TCP 443 or stealth options.

4. Features to Look for in a VPN for Laptops​

Not every VPN client is suitable for advanced laptop use. Marketing claims are easy to make. Implementation quality is harder to verify. Focus on features that reduce real exposure.

No-Log Policy and Strong Encryption​

A no-log policy means the provider claims not to store activity records that can identify what you do online. Look for clear language. The policy should explain what is not collected, what minimal operational data may be processed, and how long any data is retained. Independent audits can help, but read their scope. An audit of one server system does not always cover every app, protocol, or business process.

Encryption should be modern and well configured. OpenVPN should use strong TLS settings. WireGuard should use its standard modern primitives. Avoid providers that still promote obsolete protocols such as PPTP for privacy or censorship bypass.

Kill Switch and DNS Leak Protection​

A kill switch blocks internet traffic if the VPN drops. This is critical in restrictive regions because a brief disconnect can expose your real IP address or DNS queries. A strong kill switch should work at the firewall or system networking level, not only inside the app interface.

DNS leak protection ensures your DNS requests go through the VPN tunnel. Without it, your ISP or local resolver may still see the domains you visit. Advanced users should test DNS behavior after every major app or OS update.

Also check IPv6 handling. Some VPNs tunnel IPv4 but leak IPv6 traffic. If the provider does not support IPv6 safely, the app should block it while connected.

Speed, Server Availability, and Censorship Bypass​

Speed is not just about comfort. Slow VPNs can make secure tools impractical, pushing users toward unsafe shortcuts. Server availability also matters. If only one server works in your region, it may become blocked or overloaded.

Look for multiple regions, automatic server selection, and manual control. In restrictive environments, the ability to rotate servers is useful. However, more servers do not always mean better service. Quality, routing, and resistance to blocking matter more than raw server count.

5. Common Misconceptions About VPNs for Laptop Download​

VPNs are powerful, but misunderstandings can lead to poor decisions. Advanced users should separate useful protection from unrealistic promises.

Myth 1: A VPN Provides Complete Anonymity​

A VPN hides your traffic from the local network and masks your IP address from websites. It does not make you fully anonymous. Browser fingerprints, account logins, cookies, payment records, malware, and user behavior can still identify you.

If you log in to a personal account, that service knows who you are. If your browser has a unique fingerprint, sites may track you across IP changes. If your laptop is compromised, the VPN cannot protect data before it enters the tunnel.

VPN laws vary. In many countries, VPNs are legal privacy tools. In others, they are restricted, regulated, or blocked. Some governments allow only licensed services. Others may punish use during sensitive periods.

Do not rely on outdated forum posts. Laws and enforcement practices change. Review current local information and consider your personal risk level.

Myth 3: Free VPNs Are Always Unsafe, and Paid VPNs Are Always Safe​

The free-versus-paid debate is more complex than it seems. Some free VPNs fund operations through ads, tracking, or limited data plans. That can be a poor fit for privacy. Yet payment alone does not guarantee good security. A paid provider can still keep excessive logs, use weak apps, or offer poor support.

Evaluate the model. Ask how the service is funded, what data it collects, what limits apply, and whether it requires registration. A VPN with free access and no registration can reduce account-linked exposure, but users should still test leaks and review technical safeguards.

6. Enhancing Security Measures Beyond VPNs​

A VPN is one layer. For users in high-risk regions, security should be layered. Combine network privacy with safer browsing, device hardening, and cautious habits.

VPN with Tor for Added Anonymity​

Tor routes traffic through multiple volunteer relays. It can provide stronger anonymity than a VPN alone, but it is slower and may attract attention on some networks. There are two common models:

  • VPN then Tor: You connect to the VPN first, then open Tor Browser. Your ISP sees the VPN, not direct Tor use. The VPN sees your IP, but not your Tor destination.
  • Tor then VPN: This is more complex and less common. It may help in special cases but can also weaken anonymity if configured poorly.

For most users, Tor Browser over a trusted VPN is simpler. Do not install random browser extensions into Tor Browser. They can break fingerprint protection.

Firewalls, Antivirus, and Endpoint Security​

A VPN cannot stop malware, phishing, or malicious documents. Keep your operating system updated. Use reputable antivirus or endpoint protection where appropriate. Enable the built-in firewall and block unnecessary inbound connections.

Advanced users should also review application permissions. A messaging app, browser extension, or cracked software package can leak more than your ISP ever could. Avoid pirated VPN clients. They are a common malware vector.

Best Practices for Public Wi-Fi with a VPN​

Public Wi-Fi is risky because local attackers may monitor traffic, spoof captive portals, or attempt device discovery. A VPN reduces exposure, but habits still matter:

  • Disable auto-join for unknown networks.
  • Use HTTPS websites and secure apps even when the VPN is on.
  • Enable the VPN before logging in to email, banking, or work tools.
  • Avoid accepting unknown certificates.
  • Turn off file sharing and AirDrop-like discovery features.
  • Use your phone hotspot if the Wi-Fi network seems hostile.

secure laptop vpn on public wifi

7. Top Considerations When Choosing a VPN Provider​

Choosing a provider is a trust decision. You are moving visibility from the local network to the VPN operator. That does not mean VPNs are unsafe. It means the provider’s reputation, design, and transparency matter.

Reputation and User Reviews​

Look for long-term reputation, consistent app updates, and clear privacy documentation. User reviews can reveal connection problems in specific countries or on specific laptop platforms. However, reviews can be manipulated. Give more weight to detailed technical reports than generic praise.

Check whether the provider responds to security issues. A good provider fixes bugs, explains changes, and updates clients promptly. Silence after a serious vulnerability is a warning sign.

Customer Support and Reliability​

Support matters more in restrictive regions because blocks change. You may need new servers, alternate protocols, or manual configuration files. Useful support should offer practical steps, not only scripted replies.

For advanced users, documentation is part of support. Look for setup guides, protocol notes, troubleshooting pages, and clear explanations of kill switch behavior. If a VPN provides Linux configuration, WireGuard files, or OpenVPN profiles, it should explain how to use them safely.

Why Consider BeFreeVPN for Laptop Access​

BeFreeVPN is positioned for users who need simple access without barriers. Its key benefits include free access, no registration, and security features aimed at helping users bypass censorship effectively. No registration can be useful because it reduces account setup friction and avoids linking routine VPN use to an email address.

For laptop users, that matters. When a network blocks information quickly, the ability to download and connect without a long onboarding flow can save time. As with any VPN, advanced users should still test DNS behavior, confirm kill switch settings, and choose the protocol that works best on the local network.

FAQ: VPN for Laptop Download Questions​

What is the safest way to download a VPN for a laptop?​

Use the provider’s official website or a trusted app store. Verify the installer signature when possible. Avoid third-party download sites, cracked clients, and unknown mirror links.

Which VPN protocol is best for censorship-heavy regions?​

OpenVPN TCP 443 with obfuscation is often reliable on restrictive networks. WireGuard is usually faster, but it may need stealth features when deep packet inspection is active.

Can a VPN make me completely anonymous?​

No. A VPN masks your IP address and encrypts traffic between your laptop and the VPN server. It does not erase browser fingerprints, account logins, cookies, malware, or personal behavior patterns.

Should I use a free VPN on my laptop?​

It depends on the provider. Review its logging policy, funding model, permissions, and technical protections. Free access can be useful, especially without registration, but you should still test for leaks and connection stability.

Why does my VPN connect but websites remain blocked?​

The server IP may be blocked, DNS may be leaking, or the protocol may be fingerprinted. Try another server, enable DNS leak protection, switch protocols, or use an obfuscated mode if available.

Conclusion​

A VPN for laptop download is not just an app choice. It is a security decision that involves protocols, installation hygiene, leak protection, server reliability, and local legal context. In restrictive regions, advanced users should prioritize flexible protocols, strong kill switch behavior, DNS protection, and a provider that reduces friction when access is limited. Experience the freedom to browse without borders by downloading BeFreeVPN for your laptop today—it's free, requires no registration, and offers robust security to bypass censorship effectively.

Unveiling the best paid VPNs of 2026: a comprehensive guide

· 17 min read

Navigating digital restrictions requires the right tools—discover which paid VPNs in 2026 are worth your consideration. This deep dive into the best paid vpn 2026 options focuses on security architecture, protocol choice, audit posture, performance reliability, and, most importantly, how premium VPN services help users bypass censorship in restrictive regions without sacrificing too much speed or usability.

A paid VPN is not magic. It cannot make unsafe behavior safe, and it cannot guarantee access in every country or network. However, the right service can hide DNS queries, encrypt traffic over hostile networks, rotate exit locations, and use obfuscation to make VPN traffic harder to identify. For advanced users, the best choice depends less on advertising claims and more on protocol design, operational transparency, server reach, and resilience against blocking.

best paid vpn protocol comparison

1. Understanding VPN Protocols in 2026​

VPN protocols define how your device builds an encrypted tunnel to a remote server. In 2026, the market is still shaped by a few core technologies: WireGuard, OpenVPN, IKEv2/IPsec, and proprietary protocol variants built on similar cryptographic principles.

WireGuard: fast, lean, and widely adopted​

WireGuard remains the default performance choice for many paid VPNs. It uses modern cryptography, including ChaCha20 for symmetric encryption, Poly1305 for authentication, Curve25519 for key exchange, and BLAKE2s for hashing. Its small codebase is easier to audit than older protocols, and it reconnects quickly when users switch between Wi-Fi and mobile networks.

However, classic WireGuard has a privacy design challenge: servers need to know which public key belongs to which internal VPN IP address. Reputable providers address this with double NAT systems, ephemeral key handling, or custom account-token layers. Advanced users should check how a provider implements WireGuard rather than assuming all WireGuard deployments are equal.

OpenVPN: mature and flexible​

OpenVPN remains important because it is highly configurable and battle-tested. It can run over TCP or UDP and can be wrapped in additional layers to look more like ordinary HTTPS traffic. Its common encryption stack includes AES-256-GCM or AES-256-CBC with HMAC-based integrity, depending on configuration.

The downside is performance. OpenVPN usually has more overhead than WireGuard. Still, in restrictive networks, its flexibility matters. OpenVPN over TCP 443 can sometimes pass where raw WireGuard is blocked, although sophisticated censorship systems may still detect it.

IKEv2/IPsec: stable for mobile, weaker for stealth​

IKEv2/IPsec is reliable on mobile devices because it handles network changes well. It can be useful for users who frequently move between cellular and Wi-Fi. Yet it is not usually the best protocol for bypassing censorship. IPsec traffic has recognizable patterns and can be easier to block on restrictive networks.

Proprietary and stealth protocols​

Many leading services now offer branded protocols. Examples include NordVPN’s NordLynx, ExpressVPN’s Lightway, and obfuscation modes from providers such as Proton VPN, Surfshark, and others. These protocols vary. Some are built around WireGuard. Others use TLS-like handshakes or custom transport layers.

The key question is not whether a protocol is proprietary. The question is whether its design has been publicly documented, independently audited, and tested under censorship pressure.

Protocol comparison for censorship resistance​

ProtocolMain strengthCommon weaknessBest use case
WireGuardHigh speed, low latency, modern cryptoEasier to fingerprint unless obfuscatedStreaming, gaming, general secure browsing
OpenVPN UDPReliable security, broad compatibilitySlower than WireGuardGeneral privacy and fallback connectivity
OpenVPN TCP 443Can mimic HTTPS portsTCP-over-TCP can reduce speedNetworks blocking most VPN traffic
IKEv2/IPsecStable roaming on mobileOften identifiable and blockableMobile users on normal networks
Stealth/obfuscated modesBetter at bypassing censorshipMay reduce speed and transparencyHigh-censorship regions

For users in restrictive regions, the strongest setup is often not the fastest protocol. It is the protocol that survives active probing, deep packet inspection, DNS tampering, and IP blocking.

2. Top Features to Look for in a Paid VPN​

A premium VPN should earn its subscription fee through verifiable privacy practices, robust infrastructure, and tools that work under pressure. The following features matter most in 2026.

No-log policies and data protection​

A no-log policy should be more than a slogan. Look for providers that clearly state what they do not collect: browsing history, DNS queries, source IP addresses, connection timestamps tied to accounts, and traffic content. Also check what they do collect, such as payment records, device counts, app diagnostics, or bandwidth totals.

The strongest services support privacy-friendly payment methods, minimal email requirements, diskless or RAM-only servers, and regular third-party audits. A legal jurisdiction with strong due process can help, but jurisdiction alone is not enough. Technical design matters more than marketing.

Speed and server availability worldwide​

Server count is useful, but location quality matters more. A provider with fewer well-maintained servers may outperform a larger network with congested locations. Advanced users should inspect:

  • Physical versus virtual server locations.
  • Availability of nearby exit nodes.
  • IPv6 support or IPv6 leak protection.
  • DNS resolver ownership.
  • Multi-hop routing options.
  • Consistency during regional peak hours.

For censorship bypass, nearby uncensored countries are often critical. A user in a restrictive region may benefit from stable servers in neighboring jurisdictions because distance affects latency.

Split tunneling and advanced routing​

Split tunneling lets some apps use the VPN while others connect directly. It improves usability and can reduce suspicion on networks where all-VPN traffic is unusual. For example, a user may route a browser, messaging app, and DNS through the VPN while allowing local banking or work tools to remain outside the tunnel.

Advanced split tunneling should support both app-based and IP-based rules. On desktop systems, command-line or configuration-file support is a major advantage.

Kill switch, DNS control, and leak prevention​

A kill switch blocks internet traffic if the VPN disconnects. This is essential in high-risk environments. The best implementations are firewall-based, not just app-level toggles. DNS leak protection is equally important. If your DNS requests go to a local ISP while your browser traffic goes through a VPN, censorship systems may still infer what you are trying to access.

Obfuscation and bridge-like access​

In countries that block known VPN protocols, obfuscation is a core requirement. Look for stealth servers, alternative ports, domain fronting-style techniques where legally and technically available, or bridge-like connection methods. Because censorship changes quickly, a provider’s ability to update infrastructure matters as much as the feature itself.

3. Evaluating the Best Paid VPNs: 2026 Edition​

There is no single best VPN for everyone. The best paid VPN service for censorship resistance may not be the best for torrenting, gaming, streaming, or enterprise travel. The following evaluation focuses on advanced users who need strong privacy, credible security design, and practical access in restricted networks.

paid vpn comparison dashboard

Comparison of leading paid VPNs​

VPN serviceStrongest fitSecurity postureCensorship-bypass notes
Proton VPNPrivacy-focused users and activistsOpen-source apps, public security posture, audit historyStealth protocol and Secure Core routing are useful in hostile networks
MullvadAnonymous account model and minimal identity exposureStrong transparency, numbered accounts, independent auditsExcellent privacy model, but streaming and some restricted networks may vary
IVPNAdvanced users who value simplicity and transparencyStrong anti-tracking stance, open-source apps, audit historyGood controls, multi-hop, but smaller network than mass-market VPNs
NordVPNBroad server reach and high performanceNordLynx, RAM-only infrastructure claims, audit historyObfuscated servers and wide geography help in many regions
ExpressVPNUsability, travel, broad device supportTrustedServer RAM-based architecture claims, Lightway protocolLightway and obfuscation can help, but performance depends on region
SurfsharkMulti-device households and broad feature setWireGuard, rotating IP options, audit historyNoBorders and camouflage-style modes target restrictive networks

This table is not a permanent ranking. VPN infrastructure changes. A blocked provider can become effective again after adding new IP ranges or stealth transports. Conversely, a previously reliable VPN can degrade when censors identify its servers.

Proton VPN​

Proton VPN is a strong candidate for users who prioritize privacy engineering. Its ecosystem is built around security-conscious users, and its apps have been open source. Features such as Secure Core route traffic through hardened jurisdictions before exiting elsewhere. This adds latency but can reduce exposure to compromised exit regions.

For censorship, Proton’s stealth-oriented protocol support is a key advantage. Users in restrictive networks should test multiple profiles: WireGuard for speed, stealth mode for blocking resistance, and Secure Core for higher-risk sessions.

Mullvad​

Mullvad stands out because it does not require a traditional user account. Users receive an account number, and the service supports privacy-preserving payment options. This reduces identity linkage. Mullvad also appeals to advanced users because of its transparent technical documentation and strong desktop controls.

Its main trade-off is convenience. It may not be the best choice for users who need streaming access or hand-holding. In censorship-heavy environments, its success can vary by country and protocol. Still, for privacy minimalism, it remains one of the strongest paid VPN options.

IVPN​

IVPN is known for a focused product and clear privacy posture. It offers multi-hop routing, anti-tracker features, and open-source clients. Its network is smaller than the largest commercial VPNs, but that can be acceptable for users who value quality over size.

For advanced users, IVPN’s strength is predictable behavior. It avoids excessive feature bloat and offers strong configuration clarity. Users in restrictive areas should confirm nearby server availability before committing to a long plan.

NordVPN​

NordVPN is often considered when users want a large server network, strong speeds, and specialized modes. NordLynx, its WireGuard-based protocol, is designed to combine performance with privacy-preserving account handling. Its obfuscated servers are relevant for censorship bypass.

The main advantage is reach. A large network can provide more fallback options when specific IP ranges are blocked. However, users should test performance from their actual region, because advertised global coverage does not guarantee local reliability.

ExpressVPN​

ExpressVPN focuses on usability and broad platform support. Its Lightway protocol is designed for fast connections and stable roaming. The provider’s RAM-based server architecture is intended to reduce persistent data exposure on servers.

For travelers and non-specialist users in restrictive regions, ExpressVPN can be practical because its apps are simple and consistent. Advanced users may want deeper configuration options than it exposes by default.

Surfshark​

Surfshark is attractive for users who need many devices under one subscription. It includes features such as split tunneling, rotating IP, and modes intended to work on restrictive networks. It is often chosen by families, small teams, and users with multiple phones, laptops, and browser profiles.

Its value depends on whether its servers remain fast in your region. Like other large VPNs, the best results usually come from testing several nearby countries and protocols.

How to choose among them​

Use this step-by-step selection process:

  1. Define your threat model. Are you avoiding ISP tracking, workplace filtering, state censorship, or targeted surveillance?
  2. Identify nearby uncensored regions. Prioritize providers with reliable servers close to you.
  3. Check stealth options. If VPN blocking is common, require obfuscation or stealth modes.
  4. Verify audit and app transparency. Prefer open-source clients or recently audited apps.
  5. Test before committing. Use monthly plans or trial periods before buying a long subscription.
  6. Prepare fallback paths. Install more than one protocol profile before entering a restrictive region.

4. Performance Tests: Speed and Reliability​

Performance claims are hard to compare because every network path is different. A meaningful VPN speed test must control variables and repeat measurements.

Testing methodology​

For advanced users, a practical methodology looks like this:

  1. Establish a non-VPN baseline on the same network.
  2. Test at least three protocols: WireGuard, OpenVPN UDP, and stealth mode if available.
  3. Use nearby, regional, and long-distance servers.
  4. Measure download speed, upload speed, latency, jitter, and packet loss.
  5. Repeat tests during morning, evening, and peak local hours.
  6. Test real tasks, not only speed-test sites: video calls, SSH, large file transfer, and web browsing.

This approach reveals more than headline download speed. For censorship bypass, connection establishment time and tunnel stability may matter more than raw throughput.

High-traffic behavior​

During high traffic, VPN servers can suffer from congestion, routing instability, or rate-limiting by upstream providers. The best paid VPNs manage this with capacity planning, server load balancing, and fast IP replacement when blocks occur.

WireGuard-based protocols often maintain better speeds under load. Yet stealth protocols may be slower because they add extra wrapping to evade detection. That trade-off is acceptable when the alternative is no access at all.

Peak-hour consistency​

Peak hours are where weaker services fail. A VPN that works at 2 a.m. but drops repeatedly at 8 p.m. is not reliable. Track three indicators:

  • Reconnect frequency: how often the tunnel drops.
  • Server switching success: how quickly you can move to another server.
  • DNS consistency: whether DNS queries stay inside the tunnel after reconnects.

If you are in a high-censorship area, also test whether the provider’s app can fetch server lists when partially blocked. Some VPNs fail not because the tunnel cannot work, but because the app cannot reach its own control infrastructure.

5. Bypassing Censorship: A Strategic Approach​

Censorship systems use multiple layers. They may block DNS, poison routing, filter SNI fields, detect protocol fingerprints, throttle suspicious flows, or block known VPN IP ranges. Therefore, the best paid VPN 2026 strategy is layered rather than dependent on one feature.

vpn bypassing censorship strategy

Technical challenges​

The most common obstacles are:

  • DNS manipulation: local resolvers return false or empty results.
  • IP blocking: known VPN server addresses are blocked.
  • Deep packet inspection: traffic patterns reveal VPN protocols.
  • Active probing: censors connect to suspected servers to confirm VPN behavior.
  • App-store restrictions: users cannot download VPN apps when already inside the restricted region.

A paid VPN helps when it offers private DNS, rotating infrastructure, stealth protocols, and direct configuration files. However, users should prepare before travel or before a censorship event escalates.

2026 adaptations against new restrictions​

VPN providers increasingly rely on adaptive transports, rotating entry points, RAM-only infrastructure, and better server discovery methods. Some services also offer alternative domains, manual WireGuard configs, or bridge-style access paths.

Still, no provider can guarantee access everywhere. In the most restrictive environments, users may need several tools: a paid VPN, encrypted DNS, Tor bridges, secure messaging apps, and offline installation files.

Recommendations for high-censorship areas​

Before entering a restrictive region:

  1. Install at least two VPN apps and export manual configurations.
  2. Save support pages, server lists, and setup guides offline.
  3. Enable the kill switch and DNS leak protection.
  4. Test stealth mode on a network that blocks standard VPN traffic.
  5. Keep a non-VPN communication channel for emergency updates.
  6. Avoid discussing sensitive activity over untrusted local services.

While connected:

  • Prefer stealth protocols over maximum-speed modes when blocking is active.
  • Use nearby uncensored countries first to reduce latency.
  • Rotate servers if speeds suddenly collapse.
  • Avoid logging into accounts that reveal identity unless necessary.
  • Keep software updated, but do not update from suspicious local mirrors.

The goal is not only access. The goal is controlled, stable, and low-leakage access.

6. Common Misconceptions About Paid VPNs​

Paid VPNs are often misunderstood. Some myths exaggerate what they can do. Others dismiss real benefits.

Myth 1: A paid VPN makes you anonymous​

A VPN hides your traffic from your local ISP and changes your visible IP address. It does not make you fully anonymous. Websites can still track browser fingerprints, account logins, cookies, payment identifiers, and behavioral patterns. For stronger anonymity, users need compartmentalization, hardened browsers, and sometimes Tor.

Myth 2: Free VPNs are always unsafe and paid VPNs are always safe​

Payment does not automatically create trust. Some paid VPNs have poor policies, weak apps, or misleading claims. Likewise, a few free services are legitimate when supported by a transparent business model. The real question is incentives. If a provider has no clear revenue model, users should ask how infrastructure is funded.

Myth 3: VPN use is always illegal in restrictive countries​

VPN legality varies by country. In some places, VPNs are legal for business and personal privacy. In others, only approved services are allowed, or use may be restricted. Users should understand local law and risk before connecting. Ethical use also matters. A VPN should protect privacy and access to information, not enable harm.

Myth 4: The most expensive VPN is the most secure​

Price is not a security metric. A higher subscription may fund better infrastructure and support, but it may also fund advertising. Evaluate audits, technical documentation, protocol choices, and incident response history.

Myth 5: More servers always means better performance​

A large network helps, but quality matters. Server load, routing, peering, censorship pressure, and DNS design all influence performance. For many users, three reliable nearby servers are more valuable than hundreds of distant ones.

FAQ: Best Paid VPNs in 2026​

What is the best paid VPN for bypassing censorship in 2026?​

There is no universal winner. Proton VPN, NordVPN, ExpressVPN, Surfshark, Mullvad, and IVPN are all credible options for different users. For heavy censorship, prioritize stealth protocols, nearby servers, leak protection, and the ability to install manual configurations.

Is WireGuard better than OpenVPN for restricted regions?​

WireGuard is usually faster, but OpenVPN can be easier to disguise in some networks. If censorship is active, use WireGuard with obfuscation or a provider’s stealth mode. Keep OpenVPN TCP 443 as a fallback.

Should advanced users pay monthly or annually?​

Start monthly if censorship resistance is your main goal. Test from your real network before buying a long plan. Annual plans can save money, but they are risky if the service becomes blocked in your region.

Can a VPN bypass every government firewall?​

No. Strong censorship systems can block VPN websites, app infrastructure, protocols, and server IPs. A VPN improves your chances, especially with stealth features, but it should be part of a broader access strategy.

What matters more: audits or open-source apps?​

Both help. Open-source apps allow public inspection, while audits provide structured third-party review. The strongest providers combine transparent clients, clear privacy policies, and repeated independent assessments.

Conclusion: Choosing the Best Paid VPN in 2026​

The best paid VPNs of 2026 combine modern protocols, audited privacy claims, reliable global infrastructure, and practical censorship-bypass tools. For advanced users, the decision should start with threat modeling and regional testing, not brand popularity. Choose WireGuard or a modern equivalent for speed, use stealth modes when blocking appears, and verify that DNS, kill switch, and server discovery features work before you need them.

To ensure seamless, unrestricted internet access, try BeFreeVPN, a free service with no registration required that excels in bypassing regional restrictions.

Understanding VPN without subscription for phone: a technical deep dive

· 16 min read

In regions where censorship is prevalent, accessing the internet freely and securely with a VPN without subscription on your phone is both a necessity and a technical challenge. This deep dive explains how no-subscription mobile VPNs work, which protocols matter, how to configure Android and iOS safely, and what trade-offs advanced users should evaluate before relying on a free, registration-free, or pay-as-you-go VPN model.

A “VPN without subscription for phone” can mean several things: a free VPN app, a registration-free service, a self-hosted tunnel, a limited trial, or a one-time configuration using open-source clients. The right choice depends on your threat model, region, device controls, network conditions, and tolerance for performance limits.

vpn without subscription for phone security

1. The Need for VPN Without Subscription on Phones​

Mobile devices are often the primary internet gateway in restrictive environments. Phones move between cellular networks, public Wi-Fi, workplace access points, and captive portals. Each network can impose different filtering, blocking, and inspection rules. As a result, a VPN on a phone is not just a convenience. It can be a core part of secure connectivity.

Challenges of internet censorship in specific regions​

Censorship and network control vary by country, operator, and even city. Common mechanisms include:

  • DNS tampering: A resolver returns incorrect or empty responses for blocked domains.
  • IP blocking: Traffic to known service addresses is dropped or reset.
  • SNI filtering: The hostname visible during older TLS handshakes is inspected.
  • Deep packet inspection: Traffic patterns are classified to detect VPN protocols.
  • App-store restrictions: VPN apps may be removed, hidden, or region-limited.
  • Throttling: Encrypted tunnels may work but become too slow for practical use.

Phones are especially exposed because users often cannot control the upstream network. A no-subscription VPN can help when users need fast deployment, minimal identity disclosure, or temporary secure access during travel.

Importance of mobile security without long-term commitments​

A subscription VPN may not be practical for every user. Payment rails can reveal identity. Recurring billing may be unavailable. App-store accounts may be region-locked. Some users also need a VPN only for short periods, such as crossing borders, joining public Wi-Fi, or accessing critical communication tools.

A VPN without a subscription reduces commitment. However, it does not automatically improve privacy. Advanced users should examine the operating model: Who runs the servers? Is registration required? Is traffic logged? Is the app open source? How are keys generated? What happens when the free tier is congested?

Use cases for VPNs without subscriptions​

Typical use cases include:

  • Temporary encrypted access on hotel, airport, or campus Wi-Fi.
  • Access to blocked messaging, news, or developer resources.
  • Avoiding local DNS manipulation on mobile networks.
  • Testing connectivity from different regions.
  • Separating routine browsing from high-risk accounts.
  • Using a self-hosted VPN endpoint without paying for a consumer VPN plan.

The key is to match the VPN model to the risk. A free app may be enough for basic Wi-Fi protection. A self-hosted WireGuard server may be better for predictable performance. A registration-free VPN may be useful when minimizing sign-up data is the priority.

2. How VPNs Without Subscription Work​

A VPN creates an encrypted tunnel between your phone and a remote server. Your phone routes selected traffic into that tunnel. The remote server then forwards it to the destination. Websites and apps usually see the VPN server’s IP address, while the local network sees encrypted traffic to the VPN endpoint.

Mechanisms of non-registration VPNs​

No-subscription mobile VPNs commonly use one of four models:

  1. Free shared service: The provider offers access without payment, often with speed, data, location, or device limits.
  2. Registration-free access: The app connects without an account. Session tokens, device keys, or anonymous credentials may be used in the background.
  3. Self-hosted VPN: You run your own server on a VPS, home router, or cloud instance and connect with a standard client.
  4. One-time or pay-as-you-go access: You avoid recurring subscription terms but may still pay for bandwidth, server time, or a temporary access code.

Non-registration does not mean “no state.” The service still needs to manage routing, abuse prevention, server capacity, and cryptographic sessions. The important question is whether any persistent identifier can be linked to your real identity.

Limiting features versus fully paid VPN options​

A VPN without subscription often has constraints. These are not always bad. Limits can prevent abuse and keep the service available. Still, advanced users should understand them.

FeatureNo-subscription VPNFully paid VPN
Account requirementOften none or minimalUsually required
Payment metadataNone if freeUsually present
Server locationsLimitedBroader selection
BandwidthMay be capped or deprioritizedUsually higher
ObfuscationVaries widelyMore likely on premium plans
SupportCommunity or basicDedicated support
Audit visibilityDepends on providerDepends on provider

A paid VPN is not automatically safer. A free VPN is not automatically unsafe. The design, jurisdiction, logging policy, app security, and operational transparency matter more than price alone.

Security implications and trade-offs​

The main trade-off is trust. A VPN hides traffic contents from local networks, but the VPN operator can observe metadata and, for non-HTTPS traffic, potentially content. Today most web traffic is HTTPS, but metadata such as connection times, server IPs, and volume can still be sensitive.

Evaluate these factors:

  • Logging policy: Does the provider explain what is collected and why?
  • DNS handling: Are DNS queries sent through the tunnel?
  • Kill switch support: Does traffic leak if the tunnel drops?
  • IPv6 behavior: Is IPv6 tunneled or blocked to prevent leaks?
  • App permissions: Does the app request more access than needed?
  • Protocol choice: Is the tunnel based on modern, reviewed cryptography?

A no-subscription VPN is useful only if it improves your specific security posture. If the app injects ads, installs root certificates, or requires invasive permissions, it may add risk instead of reducing it.

3. Technical Protocols for Mobile VPNs​

Protocol choice strongly affects censorship resistance, battery use, roaming stability, and speed. Android and iOS support several VPN frameworks, but app behavior varies.

mobile vpn protocols comparison

Overview of protocols: OpenVPN, WireGuard, and IKEv2​

OpenVPN is a mature VPN protocol that can run over UDP or TCP. It is flexible and widely supported. It can use TCP 443 to resemble ordinary TLS traffic, though deep inspection may still identify it.

WireGuard is a modern protocol with a small codebase and strong performance. It uses UDP and relies on static public keys. It is efficient on phones, usually reconnects quickly, and is popular for self-hosted setups.

IKEv2/IPsec is integrated into many mobile operating systems. It is strong for roaming because it handles network changes well, such as switching from Wi-Fi to cellular. However, it may be easier to block in some restrictive networks because it uses recognizable ports and patterns.

Selecting the right protocol for your needs​

Choose based on the network problem you face:

  • For speed and battery efficiency: WireGuard is often the best default.
  • For unstable mobile networks: IKEv2 can be reliable during network transitions.
  • For restrictive firewalls: OpenVPN over TCP 443 or obfuscated variants may work better.
  • For self-hosting: WireGuard is simple, fast, and easy to audit.
  • For compatibility with legacy infrastructure: OpenVPN remains widely available.

If censorship resistance is a priority, protocol camouflage may matter more than raw speed. A fast tunnel that is blocked is not useful.

Pros and cons of each protocol​

ProtocolProsConsBest fit
OpenVPNMature, configurable, TCP/UDP supportHeavier, can be slower, fingerprintableCompatibility and restrictive networks
WireGuardFast, lean, battery-friendlyUDP-only, static keys require careMobile performance and self-hosting
IKEv2/IPsecGood roaming, native supportRecognizable traffic, configuration complexityFrequent Wi-Fi/cellular switching

For advanced users, the best setup may include fallback profiles. For example, use WireGuard normally, then switch to OpenVPN TCP 443 if UDP is blocked.

4. Implementing a No-Subscription VPN on Your Device​

Before installing any VPN without subscription on a phone, decide which model you want: registration-free app, imported configuration, or self-hosted tunnel. Then verify that the provider or server supports your operating system version.

Step-by-step guide for Android​

  1. Define your threat model. Decide whether you need basic Wi-Fi encryption, censorship circumvention, anonymity from websites, or protection from local network monitoring.
  2. Choose the VPN model. Use a trusted registration-free VPN app, a WireGuard/OpenVPN configuration, or your own server.
  3. Install from a trusted source. Prefer official app stores or verified project repositories. Avoid modified APKs from unknown sources.
  4. Review permissions. A VPN app needs VPN profile access. It should not need contacts, SMS, microphone, or accessibility permissions for normal tunneling.
  5. Import or generate configuration. For WireGuard, import a configuration file or QR code. For OpenVPN, import an .ovpn file and certificates if required.
  6. Enable always-on VPN. On Android, use system VPN settings to keep the tunnel active.
  7. Enable block connections without VPN. This acts as a kill switch on supported Android versions.
  8. Test DNS and IP leaks. Confirm that DNS queries and IPv6 traffic use the tunnel or are blocked.
  9. Create a fallback profile. Keep a second protocol or server ready for networks that block your default setup.

Step-by-step guide for iOS​

  1. Choose a reputable app or protocol client. iOS supports VPN apps through system frameworks. WireGuard, OpenVPN clients, and IKEv2 profiles are common options.
  2. Install only from trusted channels. Use the App Store when possible. If using configuration profiles, verify their source.
  3. Add the VPN profile. Approve the iOS VPN permission prompt. This allows the app or profile to create a tunnel.
  4. Import configuration. Add WireGuard keys, OpenVPN profiles, or IKEv2 settings as required.
  5. Configure on-demand rules. Use “connect on demand” for untrusted Wi-Fi or all networks, depending on your risk model.
  6. Check DNS behavior. Ensure DNS is routed through the VPN provider or a trusted encrypted resolver.
  7. Test after network changes. Move between Wi-Fi and cellular to verify that the tunnel reconnects cleanly.
  8. Keep backup access. Store a second server profile or protocol option in case the primary endpoint is blocked.

Technical requirements and compatibility​

A working mobile VPN setup needs:

  • A supported Android or iOS version.
  • A VPN client compatible with the selected protocol.
  • Correct server address, port, keys, and certificates.
  • System time synchronization for certificate validation.
  • Network access to the VPN endpoint.
  • DNS settings that do not leak outside the tunnel.

Self-hosted users also need server hardening. Disable password SSH login, patch the operating system, restrict firewall rules, and monitor resource usage. If the server IP becomes blocked, you may need to rotate endpoints or add obfuscation.

Troubleshooting common setup issues​

  • Connection fails immediately: Check keys, credentials, server address, port, and device time.
  • Connects but no internet: Verify routing, allowed IPs, NAT, and DNS.
  • Works on Wi-Fi but not cellular: UDP may be restricted. Try TCP-based OpenVPN or another port.
  • Battery drains quickly: Reduce keepalive frequency where safe, use WireGuard, or disable unnecessary reconnect loops.
  • Some apps bypass the VPN: Check split tunneling settings and per-app VPN rules.
  • IPv6 leak detected: Tunnel IPv6 or disable it at the VPN profile level if supported.

5. Overcoming Censorship: Strategies and Tools​

Bypassing regional restrictions is not only about installing a VPN. Restrictive networks often adapt. Therefore, resilient access requires layered planning and multiple transport options.

Methods to bypass regional internet restrictions​

Common strategies include:

  • Protocol fallback: Maintain WireGuard, OpenVPN, and IKEv2 options.
  • Port selection: TCP 443 may pass where unusual ports are blocked.
  • Obfuscation: Some tools wrap VPN traffic to reduce protocol fingerprints.
  • Domain fronting alternatives: Where available and lawful, some systems route through large content networks, though support has declined.
  • Bridge or relay systems: Privacy networks may use bridge nodes that are harder to enumerate.
  • Endpoint rotation: Changing servers can help when individual IPs are blocked.

No method is universal. A network may allow one protocol today and block it tomorrow. Keep configurations updated before entering a restrictive environment.

Anonymity and encryption tools​

A VPN encrypts traffic between the phone and VPN server. It does not make you fully anonymous. For stronger privacy, combine it with:

  • HTTPS-only browsing to protect content beyond the VPN endpoint.
  • Encrypted DNS if compatible with your VPN configuration.
  • Private browser profiles to reduce cookie-based tracking.
  • Secure messaging apps with end-to-end encryption.
  • Tor Browser or onion services where appropriate and legally permitted.

Be careful with stacking tools. VPN-over-Tor, Tor-over-VPN, proxies, and private DNS each change the trust model. More layers can improve compartmentalization, but they can also create leaks or performance failures if configured poorly.

Combining VPN with other privacy tools​

For mobile users in restrictive regions, a practical layered setup might look like this:

  1. A no-subscription VPN for baseline encrypted transport.
  2. A kill switch to prevent accidental cleartext traffic.
  3. A browser with tracker protection and separate profiles.
  4. Encrypted messaging for sensitive communication.
  5. Regular configuration backups stored securely.

This approach avoids dependence on a single control. If the VPN drops, the kill switch helps. If DNS is manipulated, tunneled DNS helps. If a website tracks cookies, browser isolation helps.

6. Common Misconceptions About VPNs Without Subscription​

No-subscription VPNs are often misunderstood. Some users assume they are unsafe because they are free. Others assume they are private because they do not require sign-up. Both views are incomplete.

Are free VPNs always less secure than paid VPNs?​

No. Security depends on engineering and governance, not only pricing. A free or registration-free VPN can use strong encryption and sound practices. A paid VPN can still log excessive data or ship a weak app. Examine permissions, protocol support, privacy policy, independent audits if available, and leak behavior.

Does “no registration” mean anonymous?​

Not by itself. No registration reduces the amount of account data you provide. However, your IP address, device metadata, connection timestamps, and traffic volume may still be visible to the provider. For stronger anonymity, reduce account correlation, use privacy-preserving browsers, and avoid logging into identifying services during sensitive sessions.

Can a VPN bypass every block?​

No. Some networks block known VPN IPs, throttle encrypted tunnels, or use deep packet inspection. A VPN without subscription for phone can be effective, but reliability depends on protocol choice, server reputation, obfuscation, and local network policy.

Is a self-hosted VPN always better?​

Not always. Self-hosting gives control over keys and server policy, but it also creates a fixed endpoint tied to your infrastructure. If you log into personal cloud accounts to rent the server, the server may be linkable to you. It can also be blocked more easily if it has a single IP.

Understanding data privacy and logging policies​

Read logging policies with precision. Look for specific statements about:

  • Source IP retention.
  • DNS query logging.
  • Connection timestamps.
  • Bandwidth counters.
  • Crash analytics.
  • Third-party SDKs.
  • Law enforcement response process.

Vague claims such as “military-grade encryption” do not answer these questions. Encryption protects the tunnel. Logging policy defines what the provider may know after the tunnel is established.

Evaluating the effectiveness of no-subscription VPNs​

Test effectiveness under real conditions. Check connection stability, leak resistance, DNS behavior, latency, and access to required services. Also test failure modes. A VPN that works only when conditions are perfect may fail when you need it most.

no subscription vpn privacy tools

7. Ensuring Maximum Security on Mobile​

A VPN is one component of mobile security. Phones contain sensitive accounts, biometrics, location history, messages, and app tokens. If the device itself is compromised, a VPN cannot fix that.

Best practices for maintaining mobile VPN security​

Use these controls as a baseline:

  • Enable a strong device passcode.
  • Keep biometric unlock paired with a strong fallback password.
  • Turn on full-device encryption, which is enabled by default on modern Android and iOS devices.
  • Use always-on VPN and kill switch features where available.
  • Disable split tunneling unless you need it.
  • Remove unused VPN profiles and certificates.
  • Avoid installing root certificates unless you fully trust the issuer and understand the impact.
  • Use separate browser profiles for sensitive activity.
  • Avoid logging into personal accounts during high-risk sessions.
  • Back up VPN configurations securely, not in public folders or unencrypted notes.

Regular updates and patches​

Keep the operating system, VPN app, browser, and security-critical apps updated. Protocol implementations can have bugs. Mobile OS VPN frameworks also change over time. Updates may improve leak protection, roaming behavior, and compatibility with new network restrictions.

For self-hosted VPNs, patch the server too. Rotate keys if a device is lost. Review firewall rules after server updates. Remove old users and profiles. A forgotten VPN account is a long-lived access path into your infrastructure.

Leveraging BeFreeVPN for secure, registration-free access​

For users who need a VPN without subscription for phone, BeFreeVPN is designed around quick access without registration on Android and iOS. That model is useful when you want to reduce sign-up friction, avoid long-term commitments, and get encrypted mobile connectivity quickly.

As with any VPN, configure your phone carefully. Enable system-level VPN protections, test for leaks, and keep a fallback plan for restrictive networks. If you operate in a high-risk environment, combine the VPN with secure messaging, browser isolation, and disciplined account separation.

In short, a no-subscription VPN can be a practical and technically sound option when you understand its limits. Choose the right protocol, verify the provider’s privacy posture, harden your phone, and test before relying on it. Stay secure and bypass restrictions with BeFreeVPN, offering free access without the hassle of registration on both Android and iOS.

The ultimate guide to VPNs for free for phones: breaking through censorship

· 19 min read

In regions where internet content is carefully controlled, accessing the full web on your phone can be a challenge. Discover how free VPN technology can help you bypass these barriers efficiently. This deep dive explains how to choose, configure, and troubleshoot a vpn for free for phone use while keeping privacy, performance, and mobile security in focus.

A virtual private network is not magic. It is a set of protocols, cryptographic choices, routing decisions, and trust assumptions. Used well, a free VPN on Android or iPhone can help you reach blocked services, protect traffic on hostile Wi-Fi, and reduce exposure to network-level surveillance. Used poorly, it can leak metadata, slow down your apps, or shift trust from an ISP to an unknown provider.

Before using any circumvention tool, understand your local laws, your threat model, and the risks of connecting to restricted content. The goal is to make informed technical decisions.

vpn for phone encrypted tunnel

1. Understanding VPNs: How Do They Work?​

A VPN creates an encrypted tunnel between your phone and a remote VPN server. Instead of sending traffic directly from your mobile device to a website or app endpoint, your phone encapsulates packets and sends them to the VPN server. The server decrypts or decapsulates the traffic, forwards it to the destination, and returns responses through the same tunnel.

To the local network, your traffic generally appears to be going to the VPN server. To the destination website, your traffic appears to originate from the VPN server’s IP address. This can help when content is blocked by local IP filtering, DNS manipulation, or simple geographic restrictions.

Definition and Components of a VPN​

A phone VPN typically includes these components:

  • VPN client: The Android or iOS app, or the native VPN profile installed on the device.
  • VPN server: The remote endpoint that terminates the tunnel and forwards traffic.
  • Tunnel interface: A virtual network interface on the phone that routes selected traffic into the VPN.
  • Authentication mechanism: Credentials, certificates, pre-shared keys, tokens, or app-managed session keys.
  • Encryption suite: Cryptographic algorithms that protect data confidentiality and integrity.
  • Routing and DNS rules: Controls that determine which traffic uses the tunnel and which DNS resolvers handle lookups.

On mobile operating systems, the VPN client integrates with a system VPN API. This is important because mobile apps usually cannot create unrestricted low-level network interfaces without OS permission. Android’s VpnService and Apple’s Network Extension framework provide controlled ways to route traffic through the tunnel.

Tunneling Protocols: OpenVPN, L2TP/IPSec, and PPTP​

Different VPN protocols package traffic in different ways. The protocol affects censorship resistance, battery use, speed, and reliability.

ProtocolTypical mobile useSecurity statusNotes for censorship resistance
OpenVPNCommon in third-party appsStrong when configured wellCan run over TCP 443 to resemble HTTPS-like traffic patterns, though not fully invisible
L2TP/IPSecSupported by many systemsAcceptable but olderEasier to block because it uses recognizable ports and protocol patterns
PPTPLegacy onlyInsecureShould be avoided; weak cryptography and widely fingerprinted

OpenVPN is mature and flexible. It can use UDP for speed or TCP for networks that block UDP. It supports strong authentication and modern ciphers, but configuration matters.

L2TP/IPSec combines Layer 2 Tunneling Protocol with IPSec encryption. It is older and often easier for restrictive networks to identify because it uses common IPSec-related ports.

PPTP is obsolete. It is fast because it is lightweight, but its security weaknesses make it unsuitable for privacy. If a free phone VPN offers only PPTP, choose another option.

The Role of Encryption in VPNs​

Encryption protects the contents of your traffic inside the tunnel. However, it does not hide everything. A network operator may still see that your phone is connecting to a VPN server, the timing and volume of packets, and sometimes protocol fingerprints.

Good VPN security depends on:

  • Confidentiality: Preventing local networks from reading tunneled traffic.
  • Integrity: Preventing tampering with packets in transit.
  • Authentication: Ensuring your phone connects to the intended VPN server.
  • Forward secrecy: Reducing damage if a long-term key is compromised later.
  • DNS protection: Preventing domain lookups from leaking outside the tunnel.

In censorship-heavy regions, encryption helps prevent basic inspection. Yet advanced filtering systems may block known VPN IP addresses, detect protocol signatures, or throttle encrypted traffic. That is why protocol choice, server rotation, and DNS handling matter.

2. Why Use a Free VPN on Your Phone?​

A free VPN for phone users is attractive because the phone is often the primary internet device. In many places, mobile data is more available than fixed broadband. Phones are also used for messaging, banking, news, navigation, work, and emergency communication.

Comparative Advantages: Cost and Accessibility​

The main advantage is obvious: no subscription barrier. A free mobile VPN can be useful when you need immediate access, when payments are restricted, or when international cards are not available.

Other practical advantages include:

  • Fast deployment: Install an app or profile and connect within minutes.
  • No router configuration: The tunnel runs directly on the device.
  • Works across networks: Use it on mobile data, public Wi-Fi, campus networks, or hotel networks.
  • App-level convenience: Many mobile VPN apps include one-tap connection and automatic reconnection.

For advanced users, the value is not just “free.” It is the ability to test reachability, compare protocols, and maintain fallback connectivity without committing to one provider.

Importance for Users in Censor-Heavy Regions​

When content filtering blocks news sites, social platforms, messaging services, app stores, or documentation, a VPN can restore access by routing traffic through a less restricted network path.

A phone VPN may help against:

  • DNS poisoning or DNS blocking by using VPN-provided resolvers.
  • IP blocking when the VPN server is outside the filtered network.
  • Basic URL filtering when HTTPS and VPN encapsulation hide request details.
  • Public Wi-Fi restrictions in airports, schools, cafés, or workplaces.

However, severe censorship may use deep packet inspection, active probing, and VPN server blacklists. In those cases, a standard free VPN may work intermittently. Reliability depends on server diversity, protocol options, and how quickly the provider adapts.

Potential Limitations and How to Mitigate Them​

Free VPNs often have trade-offs. The most common are bandwidth limits, fewer server locations, congestion, ads, limited protocol choices, or weaker support.

Mitigate these limitations with practical controls:

  • Choose providers with clear privacy policies. Avoid vague claims and unknown ownership.
  • Prefer modern protocols. WireGuard, IKEv2/IPSec, and well-configured OpenVPN are better options than PPTP.
  • Enable the kill switch if available. It reduces accidental traffic leaks during drops.
  • Use secure DNS inside the tunnel. Prevent DNS queries from escaping to the local ISP.
  • Keep multiple options. Have more than one reliable free VPN app or configuration ready.
  • Test before you need it. Verify that messaging, browsers, app stores, and critical sites work.

3. Setting Up a Free VPN on Your Phone​

The exact setup depends on the provider and operating system. Still, the process follows a predictable pattern: select a trustworthy provider, install the app or profile, verify permissions, connect, and test for leaks.

free mobile vpn setup

Step-by-Step Guide for Android​

  1. Choose a reputable free VPN provider. Look for transparent terms, reasonable limits, and modern protocol support.
  2. Install from a trusted source. Prefer Google Play or the provider’s official website if Play access is blocked.
  3. Review requested permissions. A VPN app needs VPN permission, but it should not require unnecessary access to contacts, SMS, microphone, or photos.
  4. Open the app and select a server. Choose a nearby region for speed or a specific region for content access.
  5. Select the protocol if available. Start with WireGuard or IKEv2 for mobile performance. Use OpenVPN TCP 443 if UDP is blocked.
  6. Approve the VPN connection prompt. Android will show a system dialog before allowing tunnel creation.
  7. Enable Always-on VPN. Go to Android settings and set the VPN as always-on if reliability is critical.
  8. Enable “Block connections without VPN.” This Android option acts like a kill switch.
  9. Test IP and DNS behavior. Use a trusted leak test site and confirm DNS resolvers are not local ISP resolvers.
  10. Test your real apps. Browsers are not enough. Check messaging, email, app updates, and video if needed.

Step-by-Step Guide for iOS​

  1. Select a reliable free VPN app. Install from the App Store where possible.
  2. Open the app and read the privacy prompts. Avoid apps with unclear data practices.
  3. Allow VPN configuration. iOS requires approval before adding a VPN profile.
  4. Authenticate with Face ID, Touch ID, or passcode. This confirms profile installation.
  5. Choose a server and protocol. IKEv2 and WireGuard-based implementations often perform well on iPhones.
  6. Connect and verify the VPN indicator. iOS shows a VPN status icon or entry in Control Center/settings.
  7. Check DNS and IP address. Confirm that traffic exits through the expected VPN region.
  8. Review Connect On Demand options. If supported, use automatic reconnection on untrusted networks.
  9. Disable risky local network access if not needed. Reduce exposure when using public Wi-Fi.
  10. Keep the app updated. VPN profile behavior and protocol libraries change over time.

Selecting Reliable Free VPN Providers​

Advanced users should evaluate more than marketing claims. Use this checklist:

  • Does the provider explain how it funds the free tier?
  • Are data limits, speed limits, and server locations clearly stated?
  • Are there third-party audits, open-source clients, or reproducible builds?
  • Does the app support a kill switch or OS-level equivalent?
  • Does it protect DNS by default?
  • Does it avoid intrusive permissions?
  • Does it support modern mobile protocols?
  • Is registration optional or minimal?

Free does not automatically mean unsafe. But “free and opaque” is a risk. A good free VPN for phone use should be transparent about limits and should not monetize sensitive browsing data.

Ensuring Privacy Through Security Settings​

After setup, harden the configuration:

  • Turn on auto-connect for untrusted Wi-Fi.
  • Turn on kill switch or OS-level traffic blocking.
  • Disable split tunneling unless you need it and understand the leak risk.
  • Use private DNS carefully. On Android, Private DNS may conflict with the VPN’s DNS design.
  • Block IPv6 leaks if the VPN does not tunnel IPv6 properly.
  • Clear old VPN profiles you no longer use.
  • Use a privacy-focused browser and keep HTTPS-only mode enabled.

4. Technical Behind the Scenes: VPN Protocols on Mobile​

Mobile networks are unstable. Phones switch between LTE, 5G, Wi-Fi, captive portals, and power-saving states. A protocol that works well on a desktop may behave poorly on a phone if it cannot handle network changes efficiently.

In-Depth Look at Mobile-Specific Protocols​

Although OpenVPN, L2TP/IPSec, and PPTP are widely known, modern mobile VPNs often rely on protocols designed or tuned for roaming.

IKEv2/IPSec is strong for mobile because it supports MOBIKE, which helps maintain sessions when the device changes networks. For example, moving from Wi-Fi to cellular can be smoother than with older tunnels.

WireGuard uses a lean codebase and modern cryptography. It is usually fast on phones and efficient with battery. Its roaming behavior is good because endpoints can update as network paths change.

OpenVPN remains valuable because it is flexible. It can run over UDP for performance or TCP 443 when restrictive firewalls block other traffic. The downside is higher overhead and sometimes more battery usage than WireGuard.

L2TP/IPSec is mostly a compatibility fallback. It can still work, but it is less ideal for restrictive regions because network filters often identify IPSec traffic.

PPTP should be treated as deprecated. It does not provide modern security and is not suitable for anonymity or sensitive access.

How These Protocols Help Bypass Censorship​

Censorship systems often rely on a mix of DNS blocking, IP blacklists, protocol blocking, and traffic fingerprinting. VPN protocols help by changing both the route and the observable structure of traffic.

  • Route change: Traffic exits from a VPN server outside the restricted path.
  • DNS isolation: Domain lookups happen through the tunnel rather than through local resolvers.
  • Encryption: Local filters cannot easily inspect the content of tunneled traffic.
  • Port flexibility: Some protocols can use commonly allowed ports such as 443.
  • Server rotation: Changing endpoints can evade static IP blocks.

Still, no free VPN can guarantee access in every region or at every time. Advanced filtering can block known VPN infrastructure. That is why mobile users should keep updated apps and multiple protocol options.

Performance Analysis of Different Protocols on Phones​

Performance depends on CPU, signal quality, server distance, congestion, and protocol overhead. In general:

ProtocolSpeedBattery impactRoaming stabilityBest use case
WireGuardHighLow to moderateGoodDaily mobile browsing and messaging
IKEv2/IPSecHighModerateExcellent with MOBIKESwitching between Wi-Fi and cellular
OpenVPN UDPMedium to highModerate to highModerateBalanced security and compatibility
OpenVPN TCPMediumHigher under packet lossModerateNetworks that block UDP
L2TP/IPSecMediumModerateModerateLegacy compatibility
PPTPHighLowPoor securityAvoid

For advanced users, the best strategy is empirical. Test each protocol on your actual network. Measure latency, packet loss, reconnection time, app behavior, and battery drain over a normal day.

5. Common Misconceptions About Free VPNs for Phones​

Free mobile VPNs are often discussed in extremes. Some users assume every free VPN is dangerous. Others assume a VPN makes them fully anonymous. Both views are incomplete.

Privacy Concerns and the Truth Behind Them​

A VPN does not eliminate trust. It moves part of your trust from the local ISP or Wi-Fi operator to the VPN provider. That is why provider selection matters.

A trustworthy free VPN should minimize logs, explain operational data collection, and avoid selling browsing activity. However, even a privacy-focused VPN may need temporary technical data for abuse prevention, load balancing, or service reliability.

Also, a VPN does not hide everything from everyone. Websites can still identify you through logins, cookies, browser fingerprints, device identifiers, and behavioral patterns. If you sign into a personal account, the site knows it is you regardless of VPN use.

Understanding Speed Reductions​

Speed loss is normal because traffic takes a longer route and passes through encryption. On a phone, speed can also drop because of weak radio signal, background battery limits, or congested free servers.

To reduce slowdowns:

  • Use the nearest reliable server unless you need a specific region.
  • Prefer WireGuard or IKEv2 when available.
  • Use UDP-based modes unless UDP is blocked.
  • Avoid overloaded peak hours if possible.
  • Disconnect apps that sync large files in the background.

Misunderstandings About Data Limits​

A data cap does not always mean the VPN is low quality. Free providers use limits to control abuse and server costs. The key is whether the limit is clear and reasonable for your needs.

For messaging, email, and text-heavy browsing, small limits may be usable. For video, app downloads, and cloud backups, free limits can disappear quickly. Advanced users should separate critical access from high-bandwidth entertainment when using a free VPN on a phone.

FAQ: Is a VPN for Free for Phone Safe?​

It can be safe if the provider is transparent, uses modern encryption, avoids intrusive permissions, and protects DNS traffic. Avoid unknown apps with aggressive ads, unclear ownership, or requests for unrelated phone permissions.

FAQ: Can a Free Phone VPN Bypass All Censorship?​

No. A free phone VPN can bypass many common blocks, but advanced censorship can block VPN IPs or detect protocol signatures. Keep multiple protocols available and update apps regularly.

FAQ: Does a VPN Make My Phone Anonymous?​

Not by itself. A VPN hides some network-level information from local observers, but websites and apps can still track accounts, cookies, device fingerprints, and behavior.

6. Troubleshooting Common Issues with Free VPNs​

Even a well-chosen free VPN can fail under real mobile conditions. Troubleshooting should be systematic: identify whether the problem is the network, protocol, server, phone settings, or app compatibility.

mobile vpn troubleshooting

Connection Drops and How to Prevent Them​

Drops happen when the phone changes networks, enters battery-saving mode, loses signal, or when the VPN server becomes unreachable.

Try these fixes:

  1. Switch protocol. Use IKEv2 or WireGuard for better roaming. Try OpenVPN TCP if UDP fails.
  2. Change servers. The current endpoint may be blocked or overloaded.
  3. Disable aggressive battery optimization. On Android, exclude the VPN app from battery restrictions.
  4. Enable auto-reconnect. Use app settings or OS-level VPN controls.
  5. Use always-on VPN with blocking. This prevents accidental leaks during reconnects.
  6. Check captive portals. Hotel or café Wi-Fi may require browser login before the VPN can connect.

Addressing Slow Speeds and Latency​

Slow VPN performance is not always the VPN’s fault. Test baseline speed without the VPN, then compare.

Useful checks:

  • If baseline mobile data is poor, move location or switch networks.
  • If only one server is slow, try another region.
  • If all VPN servers are slow, switch protocol.
  • If latency is high, choose a geographically closer server.
  • If downloads are slow but browsing is fine, the free tier may throttle bulk traffic.

For technical testing, measure ping, jitter, DNS lookup time, and packet loss. A high download speed with bad jitter can still make calls and messaging feel unstable.

Overcoming App Compatibility Problems​

Some apps block VPN traffic, require local network discovery, or use region-specific endpoints. Others fail when DNS responses differ from expected local results.

Possible solutions:

  • Use split tunneling cautiously for apps that must bypass the VPN.
  • Clear app DNS/cache data after changing VPN regions.
  • Switch VPN servers to avoid IPs flagged by the service.
  • Disable private relay or other proxy layers if they conflict with the VPN.
  • Update the app and VPN client to fix network API issues.

If an app handles sensitive personal data, think carefully before excluding it from the VPN. Split tunneling improves compatibility but can reveal traffic to the local network.

7. Ensuring Maximum Privacy and Security​

A VPN is one layer. Strong mobile privacy requires device hygiene, account security, browser controls, and careful operational habits.

Tips for Maintaining Anonymity​

For high-risk environments, reduce linkability:

  • Do not log into personal accounts when you need separation.
  • Use privacy-focused browsers with tracker blocking.
  • Clear cookies and site data between identities.
  • Avoid reusing usernames, emails, and profile photos.
  • Disable ad identifiers where possible.
  • Keep location permissions restricted.
  • Use end-to-end encrypted messaging for sensitive conversations.
  • Avoid installing unknown APKs or configuration profiles.

Also remember metadata. Even if content is encrypted, timing and volume may reveal patterns. For example, a burst of traffic after a major event may still be observable.

Using Extra Security Features Available in Free VPNs​

Some free VPNs include useful safeguards. Enable them when available:

  • Kill switch: Blocks traffic if the VPN disconnects.
  • DNS leak protection: Forces DNS requests through the tunnel.
  • Auto-connect: Starts VPN on untrusted networks.
  • Protocol selection: Lets you adapt to blocking and performance conditions.
  • Malicious domain blocking: Filters known dangerous domains, if implemented transparently.
  • No-registration mode: Reduces account-level identifiers.

Do not enable features blindly. For example, ad blocking may route DNS through a specific resolver. Read how the feature works and confirm it matches your threat model.

Regular Updates and Why They Matter​

VPN apps depend on cryptographic libraries, OS networking APIs, and server-side configurations. Updates can patch vulnerabilities, improve censorship resistance, add new servers, and fix battery drain.

Keep updated:

  • The VPN app.
  • Android or iOS system software.
  • Browser and messaging apps.
  • Security patches and WebView components.
  • VPN profiles or configuration files.

If you manually import OpenVPN or WireGuard profiles, replace outdated configs when the provider rotates keys or changes servers. Old profiles may fail silently or use weaker settings.

Final Technical Checklist for Using a Free Phone VPN​

Before relying on a VPN for free for phone access in a restrictive region, verify the essentials:

  • The provider is transparent about the free tier.
  • The app requests only necessary permissions.
  • The protocol is modern and secure.
  • DNS queries stay inside the tunnel.
  • Kill switch or OS-level blocking is enabled.
  • The VPN reconnects after switching networks.
  • Critical apps work under real conditions.
  • You have a backup server or provider.
  • The app and phone OS are updated.
  • You understand what the VPN does not hide.

A free VPN on your phone can be a practical tool for censorship circumvention, but it works best when treated as part of a broader security model. Choose carefully, test often, and tune the protocol and privacy settings for your actual network conditions.

Explore BeFreeVPN to experience seamless connections on your phone at no cost, with no registration required, perfect for maintaining internet access in restrictive regions.

Understanding anonymous VPN for internet security: a deep dive

· 17 min read

In a world where internet freedom is constantly challenged, understanding the mechanics of anonymous VPNs becomes crucial for users in restrictive regions. An anonymous VPN for internet access is not only a convenience tool for changing location. It is a privacy layer that can reduce exposure to network monitoring, hide your real IP address from websites, and help route traffic around censorship systems. This deep dive explains how anonymous VPN services work, where they help, where they fail, and how advanced users should evaluate them before relying on one.

Anonymous VPN technology sits at the intersection of cryptography, networking, jurisdiction, operational security, and trust. It can make your traffic unreadable to a local internet service provider, but it cannot magically erase every trace of your identity. Therefore, the right way to think about an anonymous VPN is as one part of a broader privacy strategy.

anonymous vpn for internet privacy

Understanding a private VPN for internet access: bypassing censorship in restrictive regions

· 14 min read

In regions where online freedom is limited, a private VPN can be your lifeline, enabling access to uncensored information and enhanced privacy. A private VPN for internet access creates an encrypted path between your device and a remote server, helping protect traffic from local network observers, reduce censorship exposure, and reach services that may be blocked by location or policy. For advanced users, the key question is not simply whether a VPN works, but how it works, where it fails, and how protocol, routing, DNS, and operational security choices affect real-world privacy.